
Toronto · Cloud security
Cloud security services in Toronto
Cloud security services in Toronto that show which cloud resources matter, who can change them and which controls actually operate. We assess, plan approved changes and hand over evidence your technical owners can use.
Cloud security assessment, architecture review and hardening for Toronto and GTA companies, from North York to downtown, running production workloads on AWS, Azure or Google Cloud.
- BBB A+ accredited
- 18 years in business
- Mon to Fri 9 to 6, Sat 10 to 2
Get a custom proposal for your cloud security scope
Tell us your cloud platform, business requirement and review priorities. Use high-level context; keep credentials and confidential evidence out of this form.
Please do not share passwords or other sensitive details here. We never sell your contact information and we comply with Canadian privacy law
(privacy policy).
Know what needs attention and who owns the next step
A defined cloud boundary
Accounts, workloads, identities and dependencies are recorded so the review coverage is clear.
Findings with context
Observed settings and supporting evidence are connected to the business service they affect.
An implementable plan
Recommended changes have owners, dependencies and acceptance checks for technical review.
A useful handover
Review limits, approved changes and unresolved decisions remain visible to your team.
Cloud controls that can be included in your scope
Select the workstreams that match your environment. The proposal names the platforms, services and depth of review.
- Environment and responsibility mapDocument the selected accounts, subscriptions or projects and the providers and teams responsible for them.
- Identity and privileged accessReview human and workload identities, role assignments, temporary access and ownership changes.
- Network exposureExamine agreed public endpoints, network boundaries and connections between workload components.
- Data and key configurationReview storage access, encryption settings and key-management responsibilities for selected data paths.
- Deployment and secretsExamine pipeline permissions, infrastructure changes and secret handling within the approved delivery path.
- Configuration findingsReview posture-management coverage, findings and exceptions alongside available workload evidence.
- Logging and handoverCheck selected event sources and routing, then document collection gaps and operational owners.
- Hardening and validationImplement expressly commissioned and approved changes with an authorized operator, rollback planning, acceptance checks and a change record.
How cloud security engagements are scoped
Custom-scoped engagements; proposal after discovery
Cloud assessment and architecture review
Custom-scoped engagements; proposal after discovery
A defined workload, procurement requirement or cloud-control question
- Environment and access boundary
- Agreed control review
- Evidence and findings register
- Prioritized remediation plan
Cloud hardening and implementation
Custom-scoped engagements; proposal after discovery
Approved technical changes with validation and handover
- Named remediation scope
- Implementation permissions
- Rollback and acceptance checks
- Change record and outstanding decisions
Cloud governance and operational handover
Custom-scoped engagements; proposal after discovery
Control ownership across teams, providers or multiple environments
- Responsibility and evidence map
- Exception and change workflow
- Monitoring handover requirements
- Agreed review and maintenance responsibilities
Project work, recurring services, third-party tools and specialist dependencies are specified separately where required.
Access, configuration and ownership
Connect cloud findings to changes your team can evaluate
Cloud security work built around your production environment
Cloud security that starts with your production environment. Cloud security services in Toronto are the assessment, architecture review and hardening that protect the data, applications and accounts your business runs on AWS, Azure or Google Cloud. A growing SaaS product can have several cloud accounts, temporary deployment permissions and customer data moving through services owned by different teams, and an AI application adds model endpoints, retrieval stores and automated tools. Canada Create has served businesses since 2008, is BBB Accredited with an A+ rating and works from 126 Willowdale Ave. in North York. Before you approve another security product, we help you see which resources matter, who can change them and which controls are actually operating.
Our cloud security services cover six areas of work:
- Cloud security assessment: a review of the selected accounts, workloads and data stores against your business requirement.
- Identity and access: roles, keys, service accounts and the permissions that let people or tools change production.
- Configuration and exposure: public endpoints, storage permissions, network paths, encryption and key management.
- Logging and detection: whether the events you would need after an incident are recorded and reviewed.
- Hardening: approved changes planned, tested and documented with your technical owners.
- Evidence and handover: findings, decisions and remaining risks written for auditors, buyers and your own team.
Canada Create scopes cloud security assessments, architecture reviews and hardening projects for Toronto organizations and teams across Canada. Discovery starts with the business service you need to protect: a customer-facing application, an internal platform, an acquisition integration or a new enterprise contract. The proposal defines the environment, evidence, permitted checks and any commissioned implementation work. You can choose an assessment-only engagement or include approved remediation with clear responsibilities.
This service focuses on the cloud configuration and operating responsibilities behind your workloads. Discovery can consider AWS, Microsoft Azure or Google Cloud, including relevant identity systems, network boundaries, storage and deployment connections. Platform fit, specialist requirements and permitted access must be confirmed before the proposal names the services and technical depth included.
What a cloud security assessment should establish
Before the assessment starts, the written scope identifies the accounts, subscriptions or projects included, production and non-production boundaries, relevant regions and responsible owners. The report makes that coverage visible alongside the evidence available for review. Unavailable records, inaccessible resources and dependencies outside the agreed boundary remain recorded limitations, so you can decide whether further work is needed.
The findings should help your team make concrete decisions about production access, service-account permissions, customer-data boundaries and deployment privileges. Each finding connects the affected resources and observed settings to the business service at risk, the supporting evidence and the decision needed from its owner. Your engineering team can then assess both the security concern and the operational dependency before approving a change.
Cloud security posture management tools can contribute configuration findings, but a tool export is one input. We can scope a review of the checks enabled, resource coverage, exceptions and ownership behind those results. The handover separates observed settings, findings supported by additional evidence and areas that could not be verified. It also distinguishes a configuration weakness from a demonstrated exploit.
Make the cloud responsibility boundary explicit
Your provider operates parts of the platform; your organization still has controls to configure and maintain. The exact division depends on the service. AWS explains that customer responsibilities vary with the services selected. Microsoft describes the different responsibilities across IaaS, PaaS and SaaS, including the customer’s responsibility for data and identities. Google Cloud likewise calls for understanding each service and its configuration.
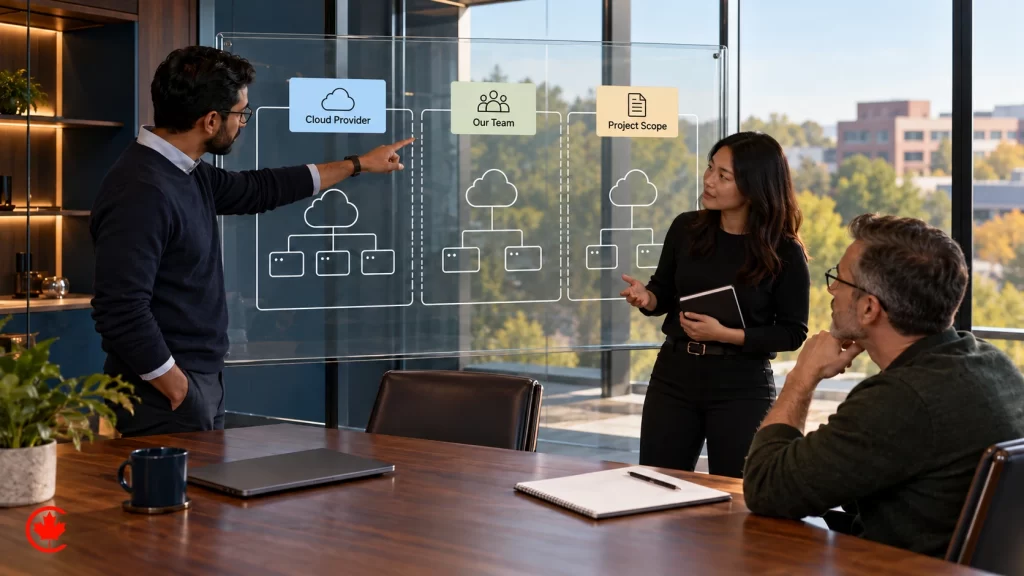
We turn that distinction into an engagement responsibility map. It identifies what the cloud provider supplies, what your team operates, what an existing managed provider handles and what this project will deliver. A control inherited from a provider is recorded alongside the customer-side configuration or evidence still needed. This gives engineering, security and procurement a common basis for discussing gaps.
Review access, exposure and change together
Human and workload identities
The agreed review can examine privileged roles, service accounts, temporary access, dormant permissions and emergency-access procedures. We look at which identities can act across environments and how ownership is tracked when staff, applications or suppliers change. Recommendations identify the affected access path and operational dependency, so a permission reduction can be reviewed before it interrupts a legitimate workflow.
Network and data boundaries
For the selected workload, we can review public exposure, inbound and outbound paths, storage permissions, encryption configuration and key-management responsibilities. The scope names the services and settings to inspect. A private endpoint or an encryption setting is considered in context with identity, access and application behaviour. Region selection, support access, copies and third-party processing are documented when they are relevant to a data-handling requirement.
Deployment and configuration changes
Cloud controls can change with the next release. An implementation scope can include reviewing infrastructure-as-code, pipeline identities, secret handling and approval paths for production changes. We agree which checks belong before deployment, which settings need ongoing review and who handles an exception. Container, Kubernetes and serverless-specific work is included only where those components are named in the proposal.
Logs and operational handover
A logging review needs a clear coverage boundary and an operational owner. The agreed scope can include event sources, routing, retention settings and evidence that selected records reach their intended destination. The handover identifies what was verified and any collection gaps. Continuing alert triage, on-call coverage and response actions belong in a separately defined operational service.
Cloud security for SaaS, AI and institutional buyers
For a SaaS team preparing for enterprise procurement, the priority may be explaining production access, customer-data boundaries and change control with evidence that engineering can maintain. For an AI product, discovery can follow the path between application identities, model-provider connections, retrieval data and tools that take actions. We define which infrastructure controls are in scope and where application authorization or AI-specific evaluation requires separate work.
For an institutional organization with several business units, the challenge may be inconsistent account ownership, inherited permissions or different providers handling each environment. A focused first engagement can examine one critical workload while recording dependencies outside that boundary. Expanding to additional environments is a deliberate scope decision, with the evidence and implementation effort made visible.
Customer questionnaires, internal policy requirements and contractual data-handling conditions can shape the review. Share the actual requirement through an agreed secure channel. Your appropriate legal, privacy or assurance advisers determine applicability and formal acceptance requirements; the technical work documents the controls and evidence within its scope.
From findings to approved changes
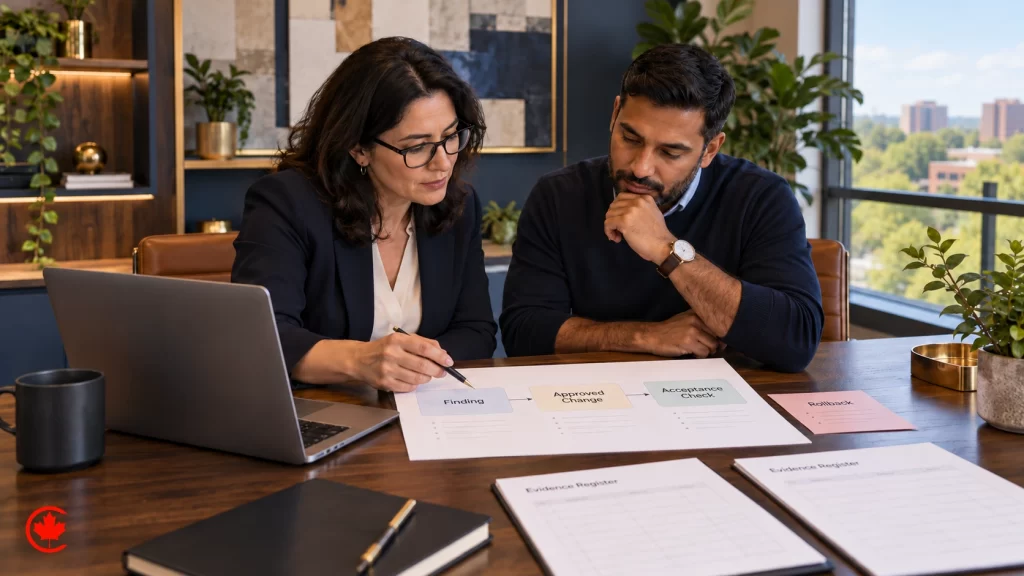
A useful finding describes the affected resource, the observed condition, its business relevance and the evidence supporting the conclusion. The remediation plan adds an owner, a proposed change, dependencies and a way to check the result. Leadership can then decide what to address now, what needs more investigation and what risk requires an explicit acceptance decision.
Assessment and implementation can be commissioned together or separately. Before a production change, we agree the authorized operator, maintenance constraints, rollback approach and acceptance checks. The record can include a before-and-after configuration comparison and a workload test selected with your application owner. An unresolved item remains visible with its next step; changing a setting does not by itself establish that the workload still functions as intended.
The final handover brings together the scope, evidence register, prioritized findings, approved change records and outstanding decisions. It identifies the review date and limitations: findings reflect the agreed coverage and available evidence at that time, and do not establish that every vulnerability has been found. Your designated owners remain responsible for outstanding remediation and maintaining the controls, unless a separate service covers that work. AI may assist analysis and report preparation under the agreed access and information-handling arrangements. Our team reviews the output and applies technical judgement before presenting final deliverables for your approval. Any runtime automation follows the separately approved operating permissions and escalation rules.
Choose the right security engagement
- Cyber security services is the starting point for selecting and coordinating a broader security program.
- Cyber security audit services review wider control evidence and risk across the agreed organization or systems.
- Penetration testing services validate exposure through separately authorized testing and rules of engagement.
- Managed security services define continuing monitoring, escalation and response responsibilities.
- Cyber security compliance consulting organizes framework-specific readiness and evidence work.
A cloud project can supply evidence or technical improvements to any of these engagements. Discovery identifies the owner of each requirement, so the work is coordinated and deliverables are not duplicated.
How to compare cloud security companies in Toronto
Many firms sell cloud security, from product vendors to managed service providers. Five questions help you compare them on the work rather than the brochure:
- Who does the work? Ask who reviews your accounts and whether they have hands-on experience with your cloud platform.
- What is delivered? A written list of findings, priorities, approved changes and evidence should be defined before work starts.
- How are findings reported? Look for reports your engineers can act on and your buyers or auditors can read.
- Who owns the accounts and keys? Your company should keep ownership of every cloud account, credential and log.
- Can you read real reviews? Live Google reviews from clients show how a firm communicates under pressure.
Be wary of any promise that an environment will be fully secure after one project. Cloud risk changes with every deployment, new service and permission, which is why the findings come with owners and a review date.
What cloud security costs in Toronto and what changes the fee
Cloud security engagements in Toronto are custom-scoped, with a proposal after discovery. Cost depends on the number and structure of environments, the services involved, available evidence, review depth and the remediation commissioned. The proposal identifies project work, any ongoing responsibilities and third-party tooling or specialist dependencies separately.
Bring a high-level description of your cloud platform, the business service at issue, existing providers and the decision date you are working toward. We can use that information to define a focused assessment or a staged implementation plan. Keep credentials, customer records and confidential security findings out of the public enquiry form.
Plan the next change
Give each finding an owner and a way to verify the result.
Connect approved remediation to your release process and operational responsibilities. Custom-scoped engagements; proposal after discovery.
From the first workload question to a documented handover
The sequence and delivery schedule are agreed around your environment, access and change constraints.
- Define the decision Discovery
Identify the business service, requesting party, platform and review priorities.
- Agree the boundary Scope approval
Confirm environments, evidence, authorized access, permitted checks and exclusions.
- Review the controls Assessment
Examine selected settings and evidence; record findings, assumptions and coverage gaps.
- Plan and validate changes Approved implementation
Assign owners and complete commissioned remediation with rollback and acceptance checks.
- Hand over the record Acceptance
Review the evidence, change log, outstanding decisions and responsibilities for maintaining controls.
Where your cloud findings can lead
Related service destinations for connected workstreams.
Cyber security program
Service overview
Select and coordinate the broader security work your organization needs.
Penetration testing
Authorized validation
Define active testing separately when the requirement calls for demonstrated exposure.
Managed security
Operational handover
Agree continuing monitoring, alert handling and response responsibilities.
A cloud engagement your technical owners can use
Workload-first scope
Start with the application or business service that creates the need for review.
Explicit responsibility
Separate provider controls, internal ownership and project deliverables.
Evidence visibility
Show observed settings, supporting records and what could not be verified.
Access discipline
Agree the permission boundary and evidence-handling route before technical work.
Cloud security in Toronto: questions buyers ask
What is cloud security for a business running on AWS, Azure or Google Cloud?
Cloud security is the work of protecting the accounts, workloads, identities, data and settings your organization runs on a cloud platform. The provider operates parts of the platform, but your team still configures and maintains its own controls. How that split falls depends on the services you use.
Do I need cloud security if my provider already secures its platform?
Usually yes, because the provider secures its infrastructure while you remain responsible for much of what you build on it. AWS explains that customer responsibilities vary with the services selected, and Microsoft describes the customer's responsibility for data and identities across IaaS, PaaS and SaaS. A cloud review makes that boundary explicit for your own accounts and workloads.
Can hackers get into a company's cloud environment?
Yes, attackers can reach cloud resources through weaknesses on the customer's side, such as broad role assignments, exposed public endpoints, poorly handled secrets in a deployment pipeline or storage with loose access settings. A review looks at human and workload identities, network exposure, data and key configuration, and who can change production. Each finding is tied to the business service it affects.
What are the downsides of running business systems in the cloud?
Visibility is the common problem. A growing SaaS product can end up with several cloud accounts, temporary deployment permissions and customer data passing through services owned by different teams, so nobody is sure who can change what. AI applications add model endpoints, retrieval stores and automated tools to that picture. A defined boundary and named owners for each control bring it back under control.
What do cloud security services include?
Work can include an environment and responsibility map, a review of identity and privileged access, network exposure checks, data and encryption-key configuration, deployment and secrets handling, and logging coverage. Hardening is available too, carried out only as approved changes with an authorized operator, rollback planning and a change record. The proposal names the platforms, services and depth of review.
Can a cloud security review cover AWS?
Yes. Discovery can consider AWS, Microsoft Azure or Google Cloud, including identity systems, network boundaries, storage and deployment connections. Platform fit and permitted access are confirmed before the proposal names the services included.
How do I choose a cloud security services provider?
Ask whether the written scope will name the exact accounts, subscriptions or projects, regions and owners covered. A useful report separates observed settings from findings backed by extra evidence and from areas that could not be verified, and it tells a configuration weakness apart from a demonstrated exploit. Treat a posture-management tool export as one input, since someone still has to check its coverage and exceptions.
Why is cloud security important for SaaS and AI teams?
Enterprise buyers and security reviewers want evidence about production access, service-account permissions, customer-data boundaries and deployment privileges. Without that, a growing team may approve another security product before knowing which resources matter and who can change them. A scoped cloud review gives engineers findings they can assess against operational dependencies before approving a change.
Bring the cloud decision you need to make
Start with your platform, business service and current concern. Custom-scoped engagements; proposal after discovery.