
Toronto · Security awareness training
Security awareness training in Toronto with phishing simulations
Security awareness training in Toronto that builds practical reporting and verification habits around the work your people do, with training, simulations and measurement scoped to your roles.
Role-based employee training and authorized phishing simulations for Toronto and GTA organizations, from North York to downtown, with clear reporting and response responsibilities.
- BBB A+ accredited
- 18 years in business
- Mon to Fri 9 to 6, Sat 10 to 2
Get your training program proposal
Custom-scoped engagements; proposal after discovery. Share the requirement and high-level scope; please do not submit credentials or sensitive operational records.
Please do not share passwords or other sensitive details here. We never sell your contact information and we comply with Canadian privacy law
(privacy policy).
What security awareness training gives you
Relevant learning
Choose topics around real job responsibilities and approved procedures.
Controlled simulations
Agree participants, themes, safeguards and approvals before campaigns.
Meaningful measurement
Read results alongside scenario difficulty, delivery conditions and limitations.
Clear reporting ownership
Connect staff reporting instructions to the designated response team.
What is included in the training program
Select employee learning, approved simulations and evidence reporting around the roles and risks in your program.
- Program scopingAgree roles, participants, delivery formats and evidence needs.
- Role-based learningSelect topics for finance, leadership, operations and technical teams.
- Simulation planningDefine authorized scenarios, destinations and campaign safeguards.
- Learning deliveryScope live, recorded or learning-system delivery with required accessibility.
- Reporting workflowIdentify the destination, owner and escalation route for suspicious messages.
- Onboarding and refreshersPlan ongoing learning around agreed risks and internal requirements.
- Measurement and interpretationDocument methodology, aggregate results and limits on comparison.
- Evidence and reviewPrepare agreed records and recommendations for the next learning cycle.
Security awareness training pricing
Custom-scoped engagements; proposal after discovery
Employee awareness program
Custom-scoped engagements; proposal after discovery
Organizations planning role-based staff learning
- Agreed role and topic plan
- Scoped delivery and administration
- Completion records
- Review recommendations
Training and simulation program
Custom-scoped engagements; proposal after discovery
Organizations adding authorized simulation and measurement
- Approved campaign plan
- Simulation safeguards
- Results with methodology and limitations
- Evidence and next-cycle review
The proposal identifies deliverables, exclusions, dependencies and any separately quoted third-party costs.
Employee learning and reporting
Practise the decisions your people face in their own roles
Security awareness training in Toronto, built around how your team works
Teach staff to spot, question and report the messages attackers send. Security awareness training in Toronto is a program of role-based lessons, authorized phishing simulations and reporting practice that helps employees verify payment changes, protect their logins, handle information carefully and report suspicious messages. Canada Create delivers these programs from our Toronto office, has served Canadian organizations since 2008 and is BBB Accredited with an A+ rating.
A security awareness program covers five areas of work:
- Program scope: roles, systems, approvals and privacy rules agreed before any simulation runs.
- Role-based training: topics for finance, front desk, executives, developers and remote staff.
- Phishing simulations: authorized campaigns that mirror the attacks your sector sees.
- Reporting workflow: a clear way to report suspicious messages, with a named response owner.
- Measurement: reporting rates and completion records, explained with their limits.
For technical testing beside training, see our cyber security audit services.
Canada Create scopes employee security awareness programs for Toronto organizations, including SaaS and AI companies, substantial healthcare, legal and insurance teams, and institutional property and capital businesses. The aim is to practise useful decisions: verifying a payment change, protecting access, handling information and reporting a suspicious message through the right channel.
This is an employer program, rather than a security-guard course or an individual professional certification. Discovery establishes the roles, work patterns, existing learning systems and evidence your organization needs. Training supports technical controls and response procedures; it does not replace them or ensure that attacks will be prevented.
Set the program boundary before a campaign
The scope records participating staff and contractors, business units, delivery formats, accessibility and language needs, administrators and reporting recipients. AI may assist lesson research, scenario drafting, design and aggregate analysis using approved inputs. Our team reviews its output with technical and editorial judgement, and your sponsor approves final training materials before use. Your designated sponsor approves the campaign plan, communications, simulation themes and schedule. Privacy, HR and security owners agree appropriate measurement, access and retention before individual-level data is collected.
Use synthetic scenarios and approved destinations. Simulations should not collect real passwords, payment information or sensitive personal records. Avoid humiliating individuals or using threatening themes that undermine staff trust. An authorized test is a learning exercise with documented safeguards, not permission for unrestricted social engineering.
Role-based topics to include where relevant
Finance, executives and assistants
Practise invoice verification, supplier bank-detail changes, executive impersonation and escalation when a request bypasses normal approvals. Training uses the organization’s approved verification steps.
Product, engineering and IT
Cover access requests, account recovery, credential handling, suspicious developer messages and reporting. For AI teams, include approved-tool boundaries and decisions about what information may be entered into an AI service.
Healthcare, legal and insurance teams
Use synthetic examples to practise recipient checks, records handling and escalation under policies approved by the organization’s privacy and compliance owners. Sector-specific legal advice remains with those advisers.
Operations and customer-facing staff
Practise suspicious attachment handling, impersonation, account-change requests and the steps to take after a mistaken click or disclosure. Make reporting practical for remote and hybrid working arrangements.
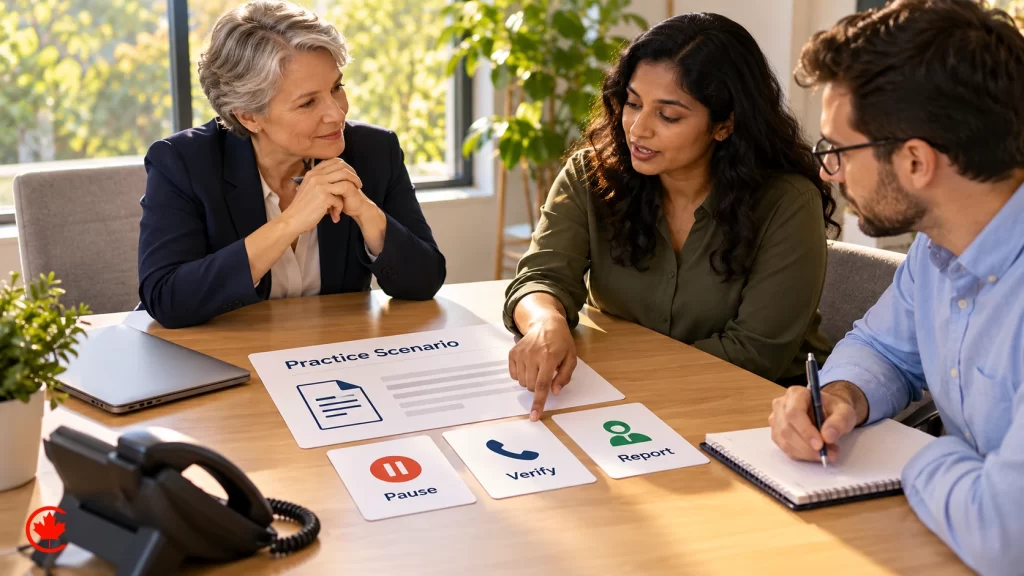
Measure learning without a misleading click-rate promise
A baseline and later simulation cycles can provide a starting point for discussion. The report should record the audience, delivery conditions, scenario difficulty and exclusions, alongside completion, reporting and interaction measures. Automated email scanning can affect link-interaction data, so platform behaviour and filtering need review before interpreting a result.
NIST’s Phish Scale guidance explains why click rates need the context of the message and intended audience. An easier campaign can lower a rate without proving stronger behaviour. Compare suitable cohorts and scenarios, include staff feedback and use findings to choose the next learning topic. Do not promise a fixed reduction or rank people publicly by a single score.
Connect reporting to a real response owner
A reporting button or mailbox only helps when someone owns the queue. Discovery identifies the destination, responsible team, triage expectations and escalation route for real suspicious messages. Configuration or testing of a reporting integration is included only when named in the scope.
Training does not itself include continuous threat monitoring or an emergency response service. If managed security is required, agree its coverage, authority and response arrangements separately. Staff should know their existing urgent-reporting route while the program is being planned.
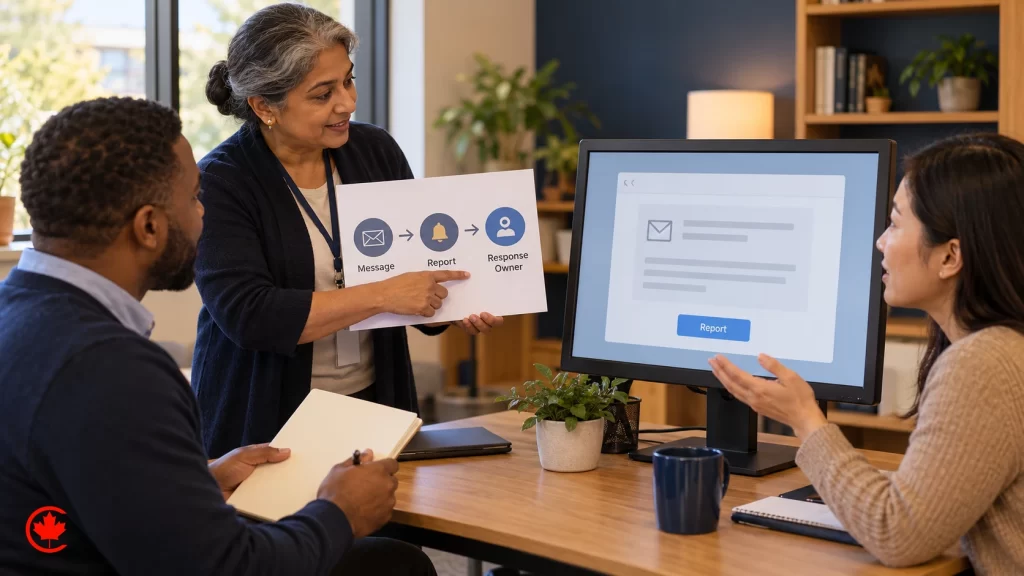
What a scoped training handover includes
- An agreed role-and-topic plan, delivery schedule and campaign approval process.
- A record of assigned learning, completion and follow-up actions.
- Simulation methodology and aggregate results with limitations explained.
- Approved reporting instructions and the named response owner.
- An evidence pack mapped to the specific customer, policy or assurance request supplied.
- Recommendations for onboarding, refreshers and the next review.
Records can support a compliance readiness program or security assessment. Completing training alone does not establish compliance, certification or insurance eligibility. Broader AI training has a separate adoption and skills scope.
Related guide: choosing a cyber security company.
What security awareness training costs in Toronto and what changes the fee
Fees are quoted in writing after discovery. The main drivers are the number of employees and roles, how many languages the material needs, whether phishing simulations are included and how often they run, the learning platform you use or need, and the reporting your auditors, insurers or board expect.
How to compare security awareness training providers in Toronto
Ask any provider these five questions:
- Who writes and runs the simulations? Find out whether templates are adapted to your sector and approved by your team first.
- What is delivered each quarter? Lessons, simulations, refreshers and reports should be named in the proposal.
- How is progress reported? Look for reporting rates and completion records, not click rates alone.
- Who owns the training records? Records and platform accounts should stay with your organization.
- What do real clients say? Read public Google reviews as well as case summaries.
Scope your employee training program
Custom-scoped engagements; proposal after discovery. Share the team size, roles, delivery preferences, current platform and reason for the program. The proposal identifies content, simulations, administration, reporting and any third-party licence costs. Frequency and timing follow the agreed risks, dependencies and internal approvals rather than a universal schedule.
Plan an approved program
Align learning, simulations and response ownership.
Discuss campaign safeguards, delivery options and the evidence your organization needs. Custom-scoped engagements; proposal after discovery.
How the program runs
Sequence and timing depend on the agreed scope, evidence and approvals.
- Discover team needs Team discovery
Review roles, work patterns, current tools and the program objective.
- Approve safeguards Campaign approval
Confirm sponsor, participants, themes, data handling and reporting recipients.
- Prepare delivery Delivery preparation
Configure only the learning and reporting components in the agreed scope.
- Train and practise Approved learning cycle
Run approved learning and simulation activities with support instructions.
- Review the evidence Evidence review
Discuss results in context and agree the next learning priorities.
A program built for participation and useful evidence
Job-relevant lessons
A payment approver, developer and client-services employee practise different decisions.
Campaign approvals
Sponsors review participants, themes, timing and safeguards before simulations run.
Synthetic scenarios
Practise without collecting real passwords, payment details or sensitive personal records.
Contextual measurement
Interpret results with audience, difficulty, delivery conditions and platform limitations.
Security awareness training Toronto: questions buyers ask
What is security awareness training for employees?
It is an employer program that helps staff practise the security decisions they face at work: verifying a payment change, protecting their sign-in, handling information and reporting a suspicious message through the right channel. Topics follow each person's role and the approved procedures already in place. It supports technical controls and response plans and does not replace them.
What is an example of a security awareness training exercise?
A finance team might practise a request to change a supplier's bank details, checking it through the organization's approved verification steps before any payment goes out. Engineering staff might work through a suspicious account recovery request. Customer-facing staff often rehearse what to do after a mistaken click, including who to tell and how fast.
How much does security awareness training cost?
The cost depends on how many staff and roles are included, the delivery format, accessibility and language needs, and whether authorized phishing simulations and measurement are added. Any learning platform or third-party fees are listed separately. Canada Create scopes the program in discovery and quotes it in a written proposal.
Is free security awareness training enough for a business?
Free general courses can cover the basics, but they cannot teach your own approval steps, your reporting mailbox or the requests your finance team actually receives. A program built around your roles uses your verification procedures and connects every report to a named response owner. Some organizations start with free material and add role-based learning where the risk is highest.
How often should security awareness training be run?
New staff should get it during onboarding, with refreshers on a schedule your organization agrees based on its risks and internal requirements. Each cycle should use what the previous one showed, including staff feedback, to choose the next topic. Running it as a one-off event rarely builds lasting reporting habits.
How do you tell whether security awareness training is working?
Compare a baseline with later cycles, reading completion, reporting and interaction measures alongside scenario difficulty and delivery conditions. NIST's Phish Scale guidance explains why a click rate means little without the context of the message and its audience. An easier campaign can lower the rate without any change in behaviour, so no fixed reduction should be promised.
Do employees receive a certificate after security awareness training?
The program produces completion records your organization can keep as evidence for reviews or customer questionnaires. It is training for your staff, which is different from an individual professional certification or a security guard course. Ask at scoping which records you need so they are collected from the first session.
How are phishing simulations run safely as part of staff training?
A designated sponsor approves the campaign plan, themes, communications and schedule before anything is sent. Privacy, HR and security owners agree what will be measured and who can see it, and simulations use synthetic scenarios that never collect real passwords, payment details or personal records. Themes that humiliate or threaten staff are left out because they damage trust.
Can security awareness training run on the learning platform we already use?
Yes, delivery can be live, recorded or through your existing learning system, with accessibility requirements agreed at scoping. The proposal states who administers the platform and which completion records come back to you.


Request a scope for security awareness training and phishing tests
Custom-scoped engagements; proposal after discovery. Tell us the requirement, current position and intended decision date.