
Toronto · Cyber security compliance consulting
PCI DSS compliance consulting in Toronto
PCI compliance consulting in Toronto that turns a card-data, buyer or assessor request into a defined readiness program: scope, gaps, implementation work and evidence responsibilities.
PCI DSS, SOC 2 and ISO 27001 readiness for Toronto and GTA organizations, from North York to downtown, with defined scope, control owners and evidence for the right external assessor.
- BBB A+ accredited
- 18 years in business
- Mon to Fri 9 to 6, Sat 10 to 2
Get your compliance proposal
Custom-scoped engagements; proposal after discovery. Share the requirement and high-level scope; please do not submit credentials or sensitive operational records.
Please do not share passwords or other sensitive details here. We never sell your contact information and we comply with Canadian privacy law
(privacy policy).
What compliance consulting gives you
A defined program
A written boundary around the service, systems, requirements and exclusions.
Owned control gaps
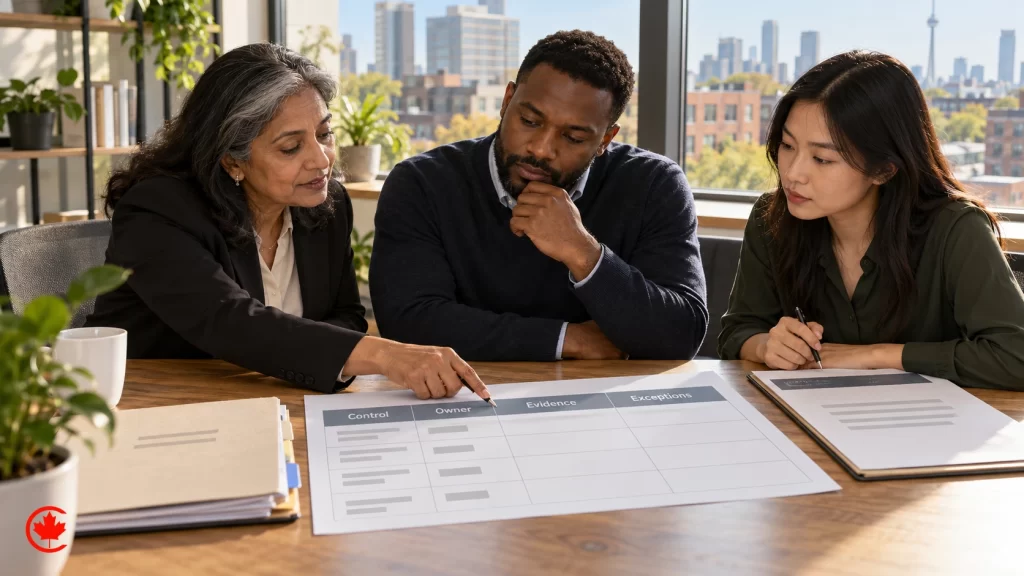
A register connecting each gap to evidence, a responsible owner and next action.
Organized evidence
Collection instructions and review responsibilities for the agreed controls.
An explicit assessor handoff
Separate readiness work from examination, certification and acceptance decisions.
What is included in compliance consulting
Readiness work is selected for the agreed program. Risk assessment and testing are expressly scoped; formal examination or certification is separately arranged with the appropriate independent provider.
- Program scopingConfirm the buyer request, service boundary and external-assessor dependencies.
- Gap assessmentReview the agreed requirements against available controls and evidence.
- Policy supportPrepare or refine documents for management review and approval.
- Implementation planningDefine technical changes, owners and dependencies before execution.
- Evidence registerIdentify sources, collection methods, review owners and record periods.
- Questionnaire supportPrepare evidence-backed responses for your organization to approve.
- Assessor preparationOrganize the agreed evidence package and unresolved-issues log.
- Maintenance planningDefine any ongoing review work as an explicit part of the proposal.
Compliance consulting pricing
Custom-scoped engagements; proposal after discovery
Readiness and implementation scope
Custom-scoped engagements; proposal after discovery
Organizations preparing a defined assurance program
- Scope and gap assessment
- Agreed policy and control work
- Evidence responsibilities
- Assessor-handoff preparation
Ongoing evidence support
Custom-scoped engagements; proposal after discovery
Organizations that need an explicitly scoped maintenance program
- Agreed review cadence
- Evidence and ownership updates
- Questionnaire support when scoped
- Preparation for the next assessor review
The proposal identifies deliverables, exclusions, dependencies and any separately quoted third-party costs.
Readiness and assessor handoff
Give each requirement an owner and an evidence trail
Turn an assurance request into a defined readiness program
Compliance readiness that starts with the exact scope your buyer or assessor needs. PCI DSS compliance consulting in Toronto is the work of preparing an organization for the Payment Card Industry Data Security Standard, and for related assurance frameworks such as SOC 2 and ISO 27001: defining which systems are in scope, finding the gaps, implementing controls and organizing the evidence an external assessor will review. Canada Create has served businesses since 2008, is BBB Accredited with an A+ rating and works from 126 Willowdale Ave. in Toronto. For merchants, SaaS teams and service providers, the first question is which service, systems and commitments the requirement covers. A framework name alone is not a workable scope.
Our compliance consulting covers six areas of work:
- Scope and boundary: the payment flow, systems, suppliers and exclusions the requirement actually covers.
- Gap assessment: each requirement mapped to current controls, evidence and an owner.
- PCI DSS readiness: card-data flow, segmentation and the self-assessment or assessor route that applies to you.
- SOC 2 and ISO 27001 readiness: policies, controls and operating evidence for an auditor or certification body.
- Implementation support: agreed remediation work, with your team’s tasks and ours kept separate.
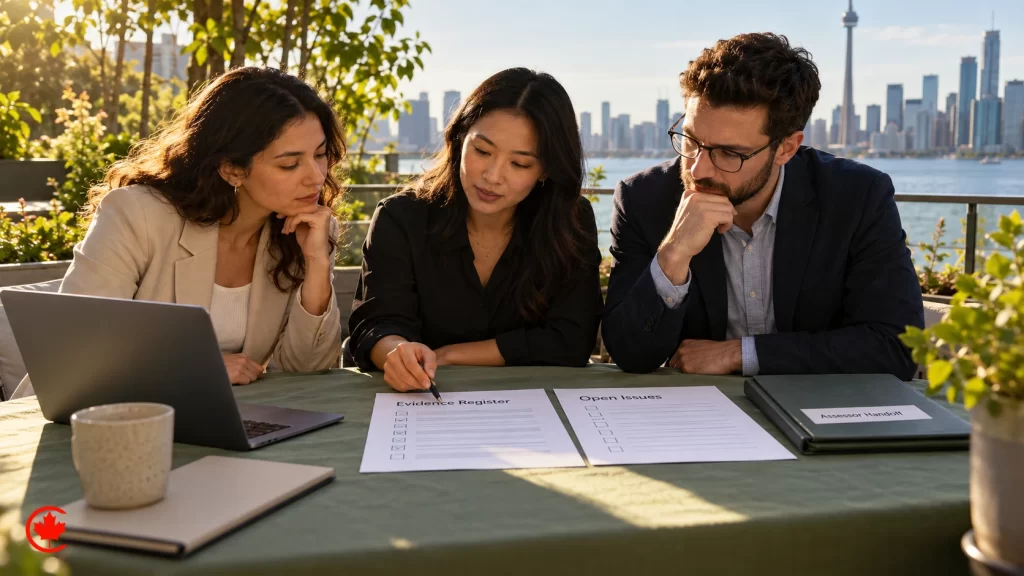
- Assessor handoff: an evidence register and open-issues log your assessor can work from.
We help organize the gap assessment, control implementation work and evidence needed for the agreed program. Your management team approves its policies, risk decisions and representations. An independent qualified provider performs any formal examination or certification. We deliver the readiness materials agreed in the proposal; the external assessor decides whether to issue an assurance report or certification, and the buyer makes its own procurement decision.
SOC 2 readiness for SaaS and service organizations
A SOC 2 engagement starts with the service being described: its infrastructure, software, people, procedures, data and relevant supplier dependencies. Discovery identifies the customer requirement, intended report users, proposed criteria, current controls and target dates to discuss with your CPA firm.
The readiness scope can include a gap register, policy and control ownership, a draft system description, evidence collection instructions and a remediation backlog. A Type I examination addresses a point in time; Type II also addresses operating effectiveness over a period. Agree the examination approach and period with your independent CPA firm rather than choosing a date from a marketing promise. The AICPA SOC resources explain the assurance role of CPAs.
For example, an access-review evidence record should identify the system, review owner, population reviewed, review date, exceptions and approvals. This is an illustrative record structure, not client evidence or a claim that a control passed. AI may help organize evidence or draft policies and questionnaire responses using inputs permitted for the project. Our team checks source support, applies technical and editorial judgement, and presents final materials for your approval before use. Generated text is not a substitute for an operating control or its records. See our SaaS SOC 2 readiness guide for procurement planning.
ISO 27001 implementation and certification readiness
ISO/IEC 27001 concerns an information security management system. Readiness work can cover its scope, risk assessment and treatment, responsibilities, the statement of applicability, policy implementation, internal review and preparation for certification-body assessment. The objective is a maintained management system with accountable owners.
Implementation support and certification are separate. A certification body makes its own assessment decision; Canada Create does not issue an ISO certificate. The official ISO/IEC 27001 overview explains the standard and certification distinction. Existing SOC 2 evidence may be useful, but overlapping work must be mapped rather than assumed to satisfy both programs.
For a practical boundary workshop, use our SaaS ISMS scope guide and its blank worksheet and fictional worked example to connect entities, activities, suppliers and exclusions.
PCI DSS readiness around your actual payment flow
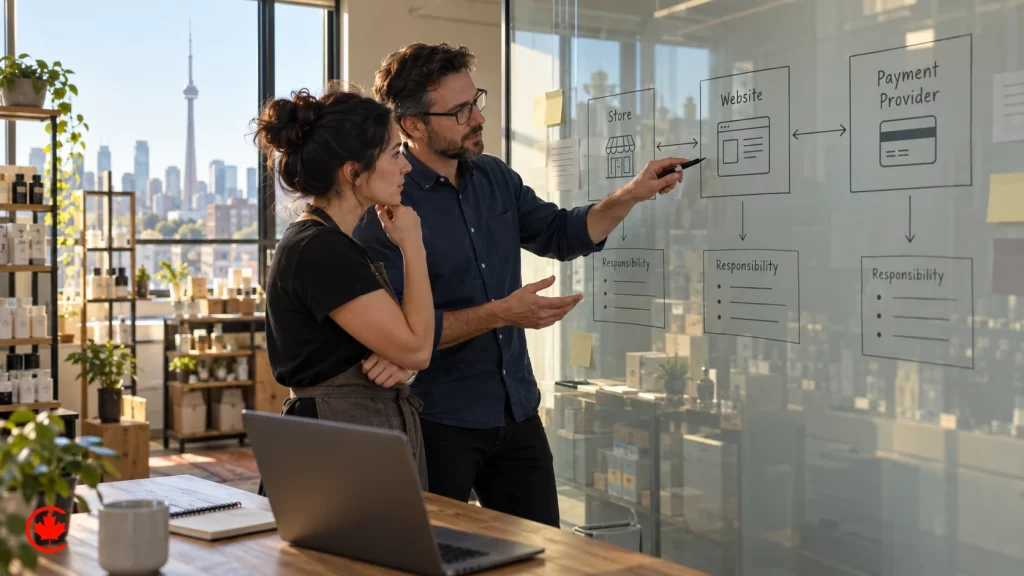
Start with how payments enter the organization and which systems, people and providers affect that flow. Scope can include payment-data mapping, responsibility mapping, gap remediation and preparation of supporting evidence. Confirm validation requirements and questionnaire eligibility with the requesting acquirer, payment brand or qualified assessor as appropriate.
PCI SSC explains that outsourcing payment processing does not remove a merchant’s responsibility for protecting account data. Equally, a readiness engagement should not assume that every merchant needs the same assessment. Any required QSA work, approved scanning or penetration testing must be identified separately. The PCI Security Standards Council merchant resources provide the official starting point.
Privacy and regulated-sector work has a separate applicability gate
PIPEDA, Quebec Law 25 and PHIPA are privacy legislation, while financial-sector requirements depend on the activity and regulator. These are obligations to assess, not certifications. We can help organize technical safeguards, data inventories and evidence against obligations your legal, privacy or compliance advisers identify. Applicability depends on the organization, activities, information and jurisdiction. Legal opinions, statutory interpretation and regulatory filings are outside a technical-readiness scope unless separately arranged with the appropriate professionals.
What a scoped handover contains
- A documented boundary covering systems, services, suppliers and exclusions.
- A gap register linking each finding to a requirement, evidence source, owner and next action.
- An implementation backlog distinguishing your team’s work, our agreed work and external-provider dependencies.
- An evidence register with collection method, review cadence and approval responsibility.
- An assessor-handoff checklist and an open-issues log that does not hide unresolved gaps.
A security audit and risk assessment, penetration test or employee awareness program can be scoped where it supports the chosen readiness program. Ongoing managed security is a separate operational service with its own agreed coverage.
Related background: PIPEDA and document transmission and choosing a cyber security company.
How to compare compliance consultants in Toronto
Compliance consultants range from solo advisors to large audit firms and software platforms. Five questions help you compare them:
- Who does the work? Ask who scopes your systems and writes the gap register, and what frameworks they have prepared organizations for.
- What is delivered? A boundary document, gap register, implementation backlog and evidence register should be named in writing.
- How is progress reported? Look for open gaps, owners and dates, not a percentage of completion.
- Who owns the evidence and accounts? Your organization should own every policy, record and tool account created for the program.
- Can you read real reviews? Live Google reviews from clients show how a consultant works with your team.
A readiness consultant prepares you; certification or a report on compliance comes from the appropriate external assessor. Be cautious of any firm that promises a pass before it has seen your environment.
What PCI and security compliance costs in Toronto and what changes the fee
Compliance engagements in Toronto are custom-scoped, with a proposal after discovery. Cost depends on the framework, the number of systems and locations in scope, how much evidence already exists and how much remediation you commission. Bring the buyer or assessor request, the systems involved, current evidence and desired decision date. The proposal identifies deliverables, responsibilities, assumptions and exclusions. External examination, certification, licences and specialist testing costs are identified separately; timing depends on the agreed scope and evidence readiness.
Plan the handoff
Connect control gaps to owners and evidence.
Discuss the work your team can complete and the external assessment you need to prepare for. Custom-scoped engagements; proposal after discovery.
How a compliance engagement runs
Sequence and timing depend on the agreed scope, evidence and approvals.
- Discover the requirement Requirement review
Review the customer or assessor request and the decision date.
- Confirm scope Scope approval
Agree systems, framework, owners, exclusions and deliverables.
- Assess the gaps Evidence review
Review existing records and distinguish verified evidence from open questions.
- Support agreed remediation Agreed implementation sequence
Coordinate the scoped control and documentation work with your team.
- Prepare handoff Assessor preparation
Organize evidence, ownership and outstanding issues for the independent assessor.
Why Toronto teams choose Canada Create for compliance readiness
Start with the buyer request
Identify the report or evidence actually requested before selecting a readiness path.
Separate the programs
SOC 2, ISO 27001 and PCI DSS retain their own scopes and assessment decisions.
Connect controls to implementation
Turn gaps into work for the system and process owners who can address them.
Keep management accountable
Policies, risk decisions and questionnaire representations remain management responsibilities.
PCI compliance in Toronto: questions buyers ask
What does PCI DSS stand for, and who maintains it?
PCI DSS stands for Payment Card Industry Data Security Standard. It is maintained by the PCI Security Standards Council and sets security requirements for organizations that store, process or transmit payment card account data.
Does my business need PCI compliance if a processor handles our card payments?
If you accept payment cards, PCI DSS applies to you in some form. The PCI Security Standards Council explains that outsourcing payment processing does not remove a merchant's responsibility for protecting account data. What changes from one business to the next is the scope and the way compliance is validated, so it helps to map how payments actually enter your organization.
Is PCI compliance mandatory for merchants in Canada?
PCI DSS is an industry standard rather than a Canadian statute, and merchants are held to it through the card brands and the agreement with their acquirer or payment processor. Canadian privacy law sits alongside it and governs personal information more broadly. Confirm your exact obligations with your acquirer.
Can a small merchant handle PCI compliance without outside help?
Many smaller merchants validate through a self-assessment questionnaire, and which questionnaire you are eligible for depends on how card data moves through your business. Your acquirer, payment brand or a qualified assessor can confirm the validation requirement before you start. Outside help is most useful when the payment flow involves several systems, providers or custom checkout code.
What happens if a business ignores PCI compliance?
Consequences are set by your acquirer or processor under the merchant agreement and the card brand rules, so ask them what applies to your account. Card data in your systems also stays exposed to the weaknesses the standard is meant to close. A readiness review shows where the gaps are before an acquirer asks.
How is PCI compliance reported to an acquirer?
Depending on the merchant's level and setup, validation is usually a self-assessment questionnaire or a report on compliance prepared by a qualified security assessor, along with an attestation of compliance. Your acquirer tells you which one it needs and where to send it. Canada Create can organize the payment-data map, gap fixes and supporting evidence, while the formal assessment stays with the qualified assessor.
What drives the cost of PCI compliance readiness?
Cost rises with the number of systems, people and providers that touch your payment flow, the size of the gaps found, and whether scanning or assessor work is required. Assessor fees, approved scanning and other outside costs are quoted separately from readiness work. Canada Create scopes each engagement during discovery and then puts the fees in writing.
Can I get a PCI compliance certificate for my business?
PCI validation is documented through the questionnaire or report your acquirer requests and the attestation that goes with it, rather than a single certificate you buy. Canada Create prepares readiness materials and does not issue certification. The acquirer, payment brand or qualified assessor makes its own decision on what it accepts.


Bring your PCI compliance requirement and decision date to discovery
Custom-scoped engagements; proposal after discovery. Tell us the requirement, current position and intended decision date.