
Toronto · Penetration testing services
Penetration testing services in Toronto
Penetration testing services in Toronto: we agree the targets, test them within written rules of engagement and give your technical and business teams a clear path from findings to fixes and retesting.
Penetration testing for Toronto and GTA organizations, from North York to downtown: web application, API, network, cloud, wireless and red team testing with clear scope and remediation priorities.
- BBB A+ accredited
- 18 years in business
- Mon to Fri 9 to 6, Sat 10 to 2
Get your penetration testing proposal
Tell us what you need tested and the requirement behind it. We will define the scope, deliverables and timing through discovery.
Please do not share passwords or other sensitive details here. We never sell your contact information and we comply with Canadian privacy law
(privacy policy).
What a penetration test gives you
Validated exposure
Evidence shows what was demonstrated within the authorized testing scope.
Actionable remediation
Findings connect affected assets, severity rationale and practical next steps.
Decision-ready reporting
Technical detail and an executive summary support engineering and procurement review.
Traceable retest results
An agreed retest links finding identifiers, verification evidence and current status.
What our penetration testing services in Toronto include
Select the testing workstreams, reporting package and follow-up that fit your systems and objectives.
- Web application and API testingAuthentication, access control, business logic and other relevant risks across agreed roles and workflows.
- External network testingAuthorized internet-facing services, remote access and perimeter exposure.
- Internal network testingAgreed starting access, lateral movement, privilege escalation and Active Directory assessment.
- Cloud testingAuthorized Microsoft 365, Azure, AWS and Google Cloud resources and connected systems.
- Wireless and physical testingWi-Fi, rogue devices, badge and tailgating scenarios within approved locations and rules.
- Social engineeringTargeted phishing and phone pretexting with approved audiences, scenarios and evidence handling.
- Red team engagementsGoal-based exercises with defined attack paths, coordination and a detection-and-response debrief.
- Remediation support and retestAgreed support, implementation responsibilities and finding-level verification after changes.
Penetration testing services: fees quoted in writing
Custom-scoped engagements; proposal after discovery
Application or network test
Quoted in writing
A defined set of applications, APIs, networks or cloud resources
- Authorized targets and rules of engagement
- Agreed testing depth and operating windows
- Technical report and executive summary
- Specified remediation support and retest scope
- Completion summary where commissioned
Red team engagement
Quoted in writing
An objective-led exercise examining agreed attack paths and detection or response
- Exercise objectives and permitted scenarios
- Defender awareness and coordination plan
- Evidence and escalation arrangements
- Executive and technical debrief
- Prioritized improvement actions
The proposal itemizes testing, reporting and follow-up. Recurring programs, engineering work and third-party dependencies are identified in the agreed scope.
Ethical hacking with a purpose
Understand the exposure, plan the fix and verify the change
Penetration testing that turns exposure into a clear action plan
A penetration test is useful when it ends in a clear list of what to fix first, and proof once it is fixed. Penetration testing services in Toronto are authorized, controlled attempts to find and exploit weaknesses in your web applications, APIs, networks and cloud environments, followed by a report your developers can act on and your leadership can understand. Canada Create has built and secured websites and systems from its office at 126 Willowdale Ave., Suite #3, in Toronto since 2008, and is a BBB Accredited Business with an A+ rating.
Our penetration testing work covers five areas, and your custom proposal names the ones you need:
- Web application and API testing: authentication, access controls, business logic and the other risks in the applications you approve.
- Network testing: the internet-facing perimeter and, from an agreed starting point, the internal network.
- Cloud testing: identity, access policies, storage and connections in the Microsoft 365, Azure, AWS or Google Cloud resources you own.
- Wireless, physical and social engineering: scenarios scoped around an approved objective and written rules.
- Reporting, remediation and retesting: evidence, severity and fixes for each finding, then verification once changes are made.
We serve Toronto organizations and teams across Canada. Developers get the detail needed to investigate and fix issues, and leadership gets a clear account of business impact, tested coverage and the next decisions.
For a SaaS product approaching an enterprise deal, a healthcare network reviewing a patient portal or an organization planning a major release, the starting point is the same: identify the systems and the decision the test must support. We agree the testing boundary, delivery plan and reporting requirements before active testing starts.
Types of penetration testing we perform
Web application and API penetration testing
Manual testing examines authentication, sessions, access controls, injection, business logic, file handling and other relevant application risks. The scope identifies applications, API versions, user roles, tenant boundaries and business workflows. We work across custom applications, WordPress and WooCommerce sites, SaaS platforms, customer portals and mobile back ends. Automated tools support coverage; manual investigation validates findings and explores relationships between weaknesses within the agreed boundary.
External network penetration testing
We assess the approved internet-facing perimeter, including remote access, exposed services, mail systems and relevant subdomains. Discovery reconciles the target inventory with system ownership. Newly identified assets are recorded for an authorization decision before being added to active testing.
Internal network penetration testing
An agreed starting position lets us examine lateral movement, privilege escalation, Active Directory weaknesses, shared credentials and paths to sensitive systems. The plan names the networks, access levels and objectives, with operating constraints for production services.
Cloud penetration testing
Cloud engagements cover agreed Microsoft 365, Azure, AWS and Google Cloud resources, including identity, access policies, storage exposure, serverless applications and connections to on-premises systems. Scope distinguishes your resources from the provider’s shared infrastructure and other tenants. Resource-owner authorization and applicable provider testing rules are checked before execution.
Wireless, physical and social engineering
We scope Wi-Fi security, rogue access point testing, badge and tailgating scenarios, targeted phishing and phone pretexting around an approved objective. Written rules identify the locations, people or groups, permitted scenarios and escalation contacts. The agreement also defines how staff information and evidence will be handled.
Red team engagements
Red team work examines a defined objective across agreed attack paths and the organization’s detection and response. The engagement sets the permitted techniques, exercise duration, defender awareness and coordination team. An executive and technical debrief connects observed activity to detection, response and improvement priorities.
Authorization and rules of engagement
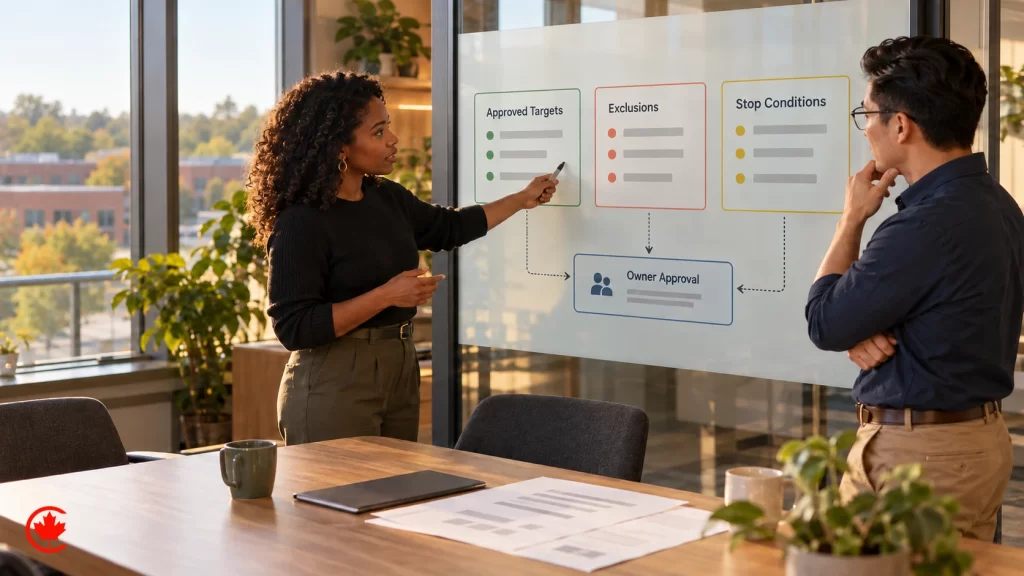
The scope names the applications, domains, networks, cloud resources and environments you authorize us to test. It records test accounts, access arrangements, exclusions and third-party approvals. For production work, the plan identifies testing windows, time zones, system owners and the support contacts needed during those windows.
Rules of engagement specify permitted techniques, boundaries for exploitation and evidence collection, and how urgent findings are escalated. Availability-sensitive activity is planned explicitly. Stop conditions identify when testing pauses, who is contacted, and who can approve resumption. Material changes to targets, techniques or access follow the agreed change process.
What you receive
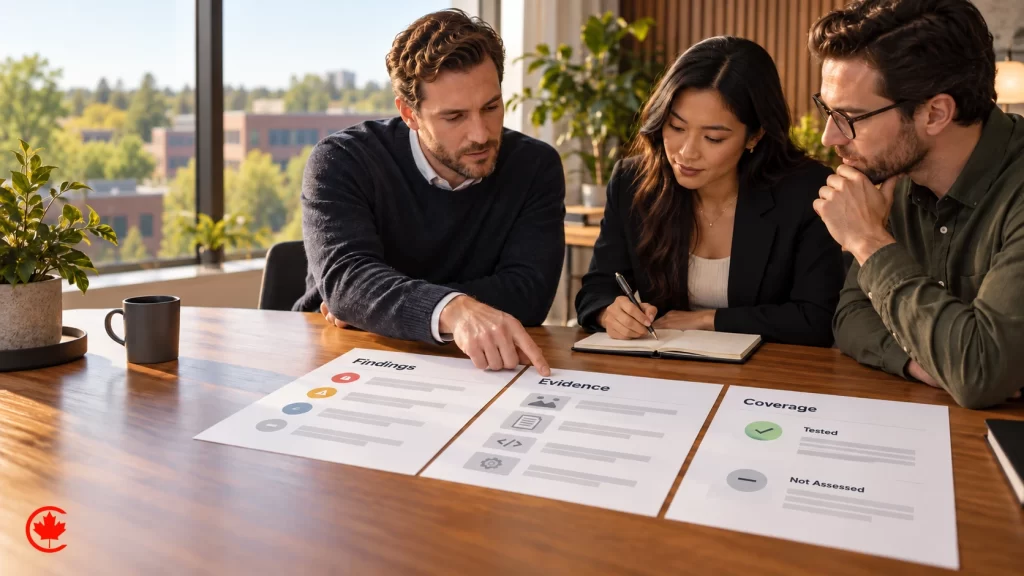
The agreed reporting package combines a technical report with an executive summary. AI may assist research, analysis and report drafting within the approved evidence-handling arrangements. Our team validates findings, applies technical judgement and presents final deliverables for your approval. Automation used during a test stays within its authorized rules of engagement. Findings have identifiers, affected assets, severity rationale, supporting evidence, reproduction detail where appropriate and recommended remediation. The summary explains observed business impact and the work to prioritize. Coverage records identify the tested environment and dates, completed checks and any areas that could not be assessed.
Reporting requirements are agreed with your technical and procurement owners at the outset. A customer or insurer may need a particular scope, report format or completion summary. Bring that requirement into discovery so the deliverables can be matched to it. Where a completion or attestation letter is commissioned, it records the actual scope, dates and finding or retest status. It does not substitute for an independent audit, certification or the recipient’s acceptance decision.
Remediation support and retesting
We help your team understand findings and plan remediation, and can implement agreed changes in systems we are authorized to manage. The proposal states the support included, implementation responsibilities and any separately scoped engineering work. Remediation owners confirm when changes are ready for verification.
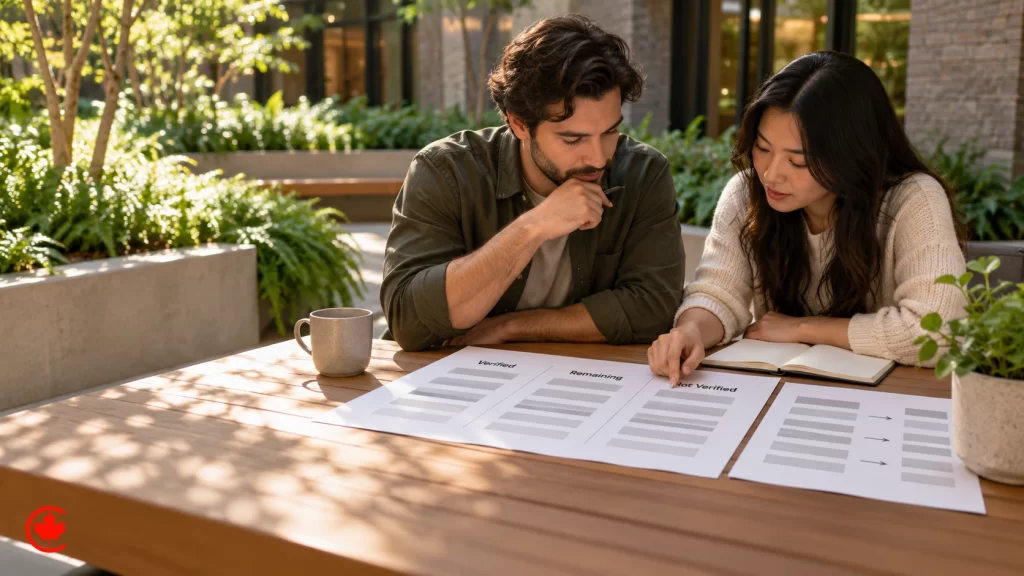
A retest scope identifies the findings to revisit, the target environment or release, the access required and the verification window. The retest record reconciles each selected finding with its original identifier and supporting evidence, distinguishing verified closure, remaining exposure and items that could not be verified. Additional testing for new features or a materially changed environment is agreed separately. This gives procurement and engineering a traceable record of what the follow-up established.
Methodology and evidence handling
The test plan selects methods appropriate to the targets and objectives, drawing on resources including the OWASP Web Security Testing Guide, the Penetration Testing Execution Standard and NIST’s technical testing and assessment guidance. The report records the approach used. The evidence-handling agreement identifies collection boundaries, approved recipients, secure transfer, storage and retention or deletion arrangements.
Who needs a penetration test
We support SaaS and technology companies, healthcare organizations, legal and accounting firms, financial services, e-commerce, manufacturing, public-sector teams and nonprofits. Common starting points include customer assurance, a product launch, a major system change, an insurance review or a defined compliance program. Testing frequency and evidence requirements are established from your risk, contractual obligations and applicable program, with your assessor or appropriate adviser involved where needed.
Testing can connect to a broader cyber security program or continuing managed security services. Those engagements define the implementation and operational responsibilities that follow the assessment.
What penetration testing costs and what changes the fee
Every engagement is quoted in writing after discovery. Price and scheduling depend on the number of applications and roles, network and cloud scope, testing depth, access readiness, reporting needs and any red team component. The proposal identifies testing, reporting, remediation support and retest inclusions so your team can compare scope and plan the work.
Related guide: choosing a cyber security company.
How to compare penetration testing companies in Toronto
Toronto has many security firms that offer penetration testing, from boutique testers to large advisory practices. Five questions help you compare them:
- Who does the testing? Ask which people will test your systems, how much of the work is manual, and which certifications those people actually hold.
- What is delivered? Look for a written scope, rules of engagement, a technical report with evidence for each finding, an executive summary and a defined retest.
- How are results reported? Findings should carry severity reasoning, affected assets and remediation steps, plus a record of what could not be tested.
- Who owns the reports and evidence? Reports belong to your organization, and evidence handling, storage and deletion should be agreed in writing.
- What do real clients say? Read the firm’s Google reviews and ask for a sanitized sample report.
Be cautious of an automated scan sold as a penetration test, or any claim that a system will be made unhackable. Our guide on what to check before hiring a cyber security company has more questions.
Book your penetration test
Tell us the business requirement, a high-level system inventory and your target decision date. We will use discovery to define the engagement and prepare your proposal. Keep credentials and confidential testing evidence for an agreed secure channel. Call (416) 273-9030, Monday to Friday, 9 am to 6 pm, and Saturday, 10 am to 2 pm. After hours, our 24/7 AI agent answers the toll-free line, +1 (800) 808-9235, and we’ll follow up the next business morning. A specialist replies within one business day. Testing-window escalation contacts are agreed separately.
Plan the follow-through
Connect findings to remediation and verification.
Agree reporting, remediation responsibilities and retest evidence before delivery. Custom-scoped engagements; proposal after discovery.
How a penetration test runs
Scope, authorization and operational readiness set the schedule. Each stage has a clear handover.
- Scoping and rules of engagement Scope approval
Agree targets, objectives, permitted techniques, testing windows, exclusions and contacts.
- Readiness and reconnaissance Authorized access
Confirm access, target ownership, operating constraints and the starting inventory.
- Testing and validation Agreed testing window
Investigate and validate exposure within the approved rules; escalate urgent findings through the agreed route.
- Reporting and remediation planning Report review
Deliver technical findings and an executive summary; review priorities, owners and recommended changes.
- Remediation and retest Agreed follow-up
Complete commissioned remediation support and verify selected findings against the agreed environment and evidence criteria.
Why Toronto organizations choose Canada Create for penetration testing
Web engineering experience
Canada Create has built and hosted web systems since 2008, connecting assessment findings with implementation context.
BBB Accredited, A+
An established Toronto agency with Better Business Bureau accreditation and an A+ rating.
Purposeful methodology
Select relevant OWASP, PTES and NIST guidance for the systems and objectives in scope.
Quoted in writing
Agree the targets, deliverables, responsibilities and fees before testing starts.
Penetration testing Toronto: questions buyers ask
What is penetration testing in technology?
Penetration testing is an authorized attempt to find and exploit weaknesses in applications, APIs, networks or cloud environments, within targets and rules you approve in advance. The report shows what was demonstrated, how severe it is and what to fix. Developers get technical detail and leadership gets a summary of business impact and tested coverage.
Can automated tools or AI replace a manual penetration test?
Automated tools help with coverage, but manual investigation is what validates findings and explores how separate weaknesses connect, especially in business logic and access control. A scanner can flag a known issue without showing whether it can actually be exploited in your setup. Canada Create uses both, with people confirming every reported finding.
Does a penetration test look for known CVE vulnerabilities?
Yes, known vulnerabilities in exposed services and software are part of the work, particularly on external and internal network tests. A penetration test goes further than a CVE list by checking authentication, sessions, permissions and the paths an attacker could chain together. Findings are tied to the affected assets with a severity rationale.
How much do penetration testing services cost?
Price depends on the number of applications, API versions and user roles, the networks and cloud resources in scope, the testing depth and any operating windows for production systems. Retesting, remediation support and red team exercises add to the scope when included. Canada Create agrees targets in discovery and itemizes testing, reporting and follow-up in a written proposal.
How do I choose a penetration testing provider in Toronto?
Ask how the provider sets rules of engagement, who carries out the testing, and what the report and retest look like. A useful report links each finding to affected assets, severity and practical next steps, and a retest ties finding identifiers to verification evidence. It is also worth confirming the tester's office location and reading recent Google reviews.
Can a penetration test help with compliance requirements?
A technical report and executive summary can support SOC 2, PCI DSS, insurance or customer security reviews. The requesting party decides what it accepts, so confirm the required test type, scope and report format with it before testing begins. A completion summary can be added when commissioned.
What kinds of penetration testing services can a business order?
Options include web application and API testing, external and internal network testing, and cloud testing across Microsoft 365, Azure, AWS and Google Cloud. Wireless and physical tests, targeted phishing and phone pretexting can be added under written rules. Red team engagements test a defined objective along with your detection and response.


Make your next security review easier to act on
Bring your systems, business requirement and decision date into discovery. We will define testing and reporting that give your team a practical next step.