
Toronto · Network security
Network security services in Toronto
Network security in Toronto, done on purpose: segments that keep guests, card terminals and cameras apart, and a diagram and admin access that belong to you.
Network security for Toronto and GTA offices, clinics and stores, from North York to downtown: firewalls, segmentation, staff and guest Wi-Fi, remote access with MFA and documentation.
- BBB A+ accredited
- 18 years in business
- Mon to Fri 9 to 6, Sat 10 to 2
Get a custom proposal for your network security
Tell us how many locations you have, who connects from home and what is on the network. We reply with a custom proposal.
Please do not share passwords or other sensitive details here. We never sell your contact information and we comply with Canadian privacy law
(privacy policy).
A documented network you can explain: what network security delivers
A network you can explain
Segments, Wi-Fi and firewall rules set up on purpose, each with a written reason.
Controlled ways in
Remote access and vendor access through named accounts with a second sign-in step.
Gear that is kept current
Firmware on firewalls, switches and access points updated on a schedule you can see.
Documentation you hold
A diagram, device inventory and admin access kept in your organization's name.
What network security includes
Each engagement is scoped in your custom proposal; these are the usual pieces.
- Firewall setup or rule reviewA firewall configured deny by default, or every existing rule checked and justified.
- Network segmentationSeparate segments for staff, guests, card terminals, cameras, IoT and servers.
- Secure staff and guest Wi-FiSeparate wireless networks, current encryption and isolated guest access.
- Remote access with MFAVPN or zero trust access with named accounts and a second sign-in step.
- Vendor access reviewOutside accounts rebuilt as named, limited access that can be switched off.
- Network gear patchingFirmware inventory, update schedule and end of support flags.
- Logging, alerts and DNS filteringRecords kept, alerts routed to a named person, harmful sites blocked at lookup.
- Diagrams and documentationNetwork diagram, device list, rule reasons and credential locations in your name.
How network security is priced
All network security work is quoted in writing after a free review. Hardware and subscriptions are paid to the vendor in your name and shown separately.
Network review
Quoted in writing
Organizations that want to know what they have
- Firewall rule read through
- Segment and Wi-Fi check
- Remote and vendor access list
- Written findings
Single office build or rebuild
Quoted in writing
One location setting up or cleaning up its network
- Firewall configuration
- Staff, guest and device segments
- MFA on remote access
- Diagram and documentation
Multi location project
Quoted in writing
Organizations with several sites
- Matching segment layouts
- Site to site connections
- Central device inventory
- Per site documentation
Ongoing network upkeep
Quoted in writing
Organizations that want the network kept current
- Firmware updates
- Rule change records
- Alert follow up
- Monthly report
Ad spend and software licences are paid to the platform directly and shown separately from our fees.
Network security guide
Firewalls, segments, Wi-Fi and remote access explained for owners
Most office networks grew by accident; a secure one is set up on purpose. Network security in Toronto is the work of controlling what can talk to what inside your office and between your office and the internet: the firewall, how the network is split into separate segments, staff and guest Wi-Fi, remote access for people at home, the patching of routers, switches and access points, and the records that show how it is all set up. It is for owners, office managers and operations leads at offices, clinics, stores and organizations with several locations who want a network that is set up on purpose and documented in their own name. Canada Create has worked with Canadian organizations since 2008, is BBB Accredited with an A+ rating and works from 126 Willowdale Ave. in Toronto, and network security sits within our cyber security services in Toronto.
Our network security services cover six areas:
- Firewall setup and rule review, with firmware patching on a schedule.
- Segmentation that keeps guests, card terminals, cameras and staff devices apart.
- Staff and guest Wi-Fi with separate keys and access points set up properly.
- Remote access through VPN or zero trust access, with MFA for every account.
- Logging, alerting and DNS filtering with a named person who receives alerts.
- Diagrams and documentation in your organization’s name.
- What owners mean by network security
- Firewall setup, rule review and patching
- Segmentation in plain words
- Wi-Fi for staff and for guests
- Remote access, MFA and outside vendors
- Logging, alerting and DNS filtering
- Small offices and several locations
- Diagrams and documentation in your name
- Where this work starts and stops
- Privacy rules and card terminals
- How a network security project runs
- What network security costs in Toronto and what changes the fee
- How to compare network security companies in Toronto
- Book a network security review and custom proposal
What owners mean by network security
When an office manager types “network security for small business” or “firewall for small business”, the question behind it is usually narrower than the words. The internet provider installed a box years ago, someone added a Wi-Fi extender, the camera installer opened a port, and now nobody is sure what is exposed. Or a new lease means a new office, and the owner wants the network built properly before staff move in. Or an insurer’s questionnaire asks about segmentation and remote access, and the answers are guesses. Day-to-day upkeep of the network is covered by network support in Toronto.
The parts of an office network
A typical small network has an internet connection, a firewall or a router acting as one, one or more switches, wireless access points, and the things plugged in: desktops, laptops, printers, phones, payment terminals, cameras, door controllers, a smart TV in the boardroom, perhaps a small server. Network security decides which of those can reach each other, which can reach the internet, and which outsiders can reach in. It is about traffic and access, not about the software on each laptop.
What a good result looks like
A well run network is boring to describe. Guest phones cannot see the printers. The card terminal sits on its own segment. Staff at home connect through a controlled path that asks for a second sign-in step. The firewall rules each have a reason written beside them. Firmware on every device is current. Someone receives the alerts and knows what they mean. And a diagram exists that a new provider could read on their first day.
Firewall setup, rule review and patching
The firewall is the gate between your network and the internet, and often between segments inside it. Many small offices run on the router their internet provider supplied, with default settings and a list of open ports nobody remembers approving.
Setting up or replacing a firewall
For a new office or a replacement, the work starts with what the organization actually needs: how many people, how many segments, whether staff connect from home, whether there are cameras or a phone system, and what internet service feeds the building. The firewall is chosen and sized to fit, configured with a deny by default posture, and its admin account is set up in the organization’s name with a strong password and a second sign-in step.
Reviewing the rules you already have
A firewall rule review reads every rule and asks three questions: what does it allow, who asked for it, and is it still needed? Old rules for a departed bookkeeper’s home connection, a port opened for a camera vendor’s support session, or a blanket rule added to make a printer work tend to stay forever. Each one is either documented with a reason or removed, and the changes are scheduled so staff are not surprised.
Patching network gear
Routers, firewalls, switches and access points run their own software, called firmware, and makers release updates for it. Network gear is often left out of the patching routine that covers laptops. A network security engagement lists every device, its firmware version and whether the maker still supports it, then sets a regular update schedule and flags equipment that is past its supported life so the owner can budget a replacement.
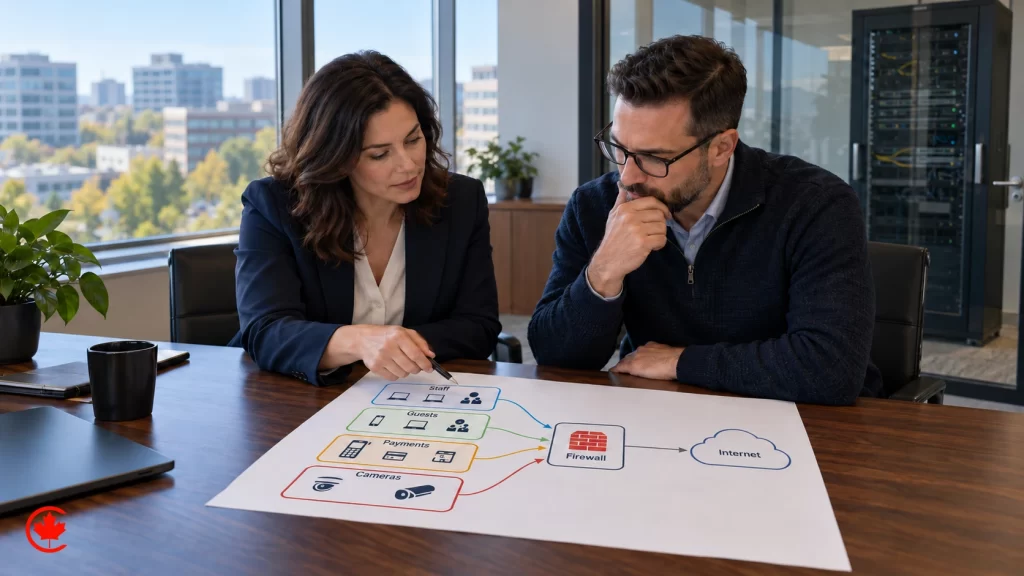
Segmentation in plain words
Segmentation means splitting one flat network into several smaller ones that cannot freely reach each other. Think of an office building: everyone uses the same front door, but the server room, the supply closet and the boardroom each have their own lock. On a network, segments are usually built as separate VLANs, with firewall rules deciding what may cross between them.
Common segments for a small organization
- Staff devices: the laptops and desktops people work on, with access to the file storage and printers they need.
- Guest Wi-Fi: internet only, with no path to anything inside.
- Payment terminals: card readers and point of sale devices kept apart from everything else.
- Cameras and IoT: security cameras, door controllers, thermostats, smart TVs and similar devices that rarely need to talk to staff laptops.
- Servers and management: anything that stores shared data, plus the admin interfaces of the network gear itself.
- Phones: desk phones on their own segment where the phone system calls for it.
Why cameras and smart devices get their own space
Cameras, smart displays and building controls are made to be easy to install, and many receive firmware updates rarely or never. Putting them on a separate segment means that if one of them is poorly made, it cannot be used as a stepping stone to the accounting laptop. It also makes it easier to see when one of them starts sending traffic it should not.
Segmenting without breaking the workday
The most common reason segmentation is skipped is fear that the printer or the scanner will stop working. A careful plan maps what each device actually needs to reach before anything moves, then makes the change after hours with a short written list of what to test the next morning: printing, scanning to email, the card terminal, the door buzzer and the camera viewer.
Wi-Fi for staff and for guests
Searches for “secure office Wi-Fi” and “guest Wi-Fi security” usually come from a reception desk that hands out the same password to staff, clients and the courier. That password ends up on sticky notes, in old phones and in the hands of people who left years ago.
Separate networks, separate passwords
Staff and guests should be on different wireless networks that lead to different segments. Staff Wi-Fi uses current encryption and, for larger teams, individual sign-ins tied to each person’s work account so access ends when someone leaves. Guest Wi-Fi gives internet access only, can carry a simple acceptance page, and can be limited in speed so a guest streaming video does not slow the office.
Clinics, waiting rooms and storefronts
A clinic waiting room, a dealership showroom or a café with customer Wi-Fi needs guest access that is truly isolated, including from other guests on the same network. Client isolation stops one visitor’s phone from seeing another’s. For storefronts, the guest network must never share a segment with the card terminals or the back office computer.
Coverage and placement
Wi-Fi security also depends on where the signal goes. Access points placed and tuned for the space keep a strong signal inside the office without spilling far into the hallway or the parking lot, and rogue devices plugged into a wall jack can be spotted. A site walk notes dead zones, old extenders and any access point that does not belong.
Remote access, MFA and outside vendors
Staff working from home, a partner checking files from a cottage, a bookkeeper who logs in on Thursdays: each is a path into the network, and each path needs a gate.
VPN or zero trust access
A VPN creates a protected tunnel from a laptop at home into the office network. It works well for small teams when it is set up with individual accounts and a second sign-in step. Zero trust access is a newer approach that gives each person access to the specific applications they need rather than to the whole network, checking who they are and what device they use each time. Which fits depends on where your files and applications live, how many people connect from outside, and whether much of the work has already moved to cloud services such as Microsoft 365.
Multi factor authentication for remote access
Every remote access path should ask for something beyond a password: a code from an app on the person’s phone, a prompt to approve, or a hardware key. This applies to the VPN, the firewall’s admin page, any remote desktop service and the router’s management portal. Shared remote accounts are replaced with named accounts so the logs show who connected.
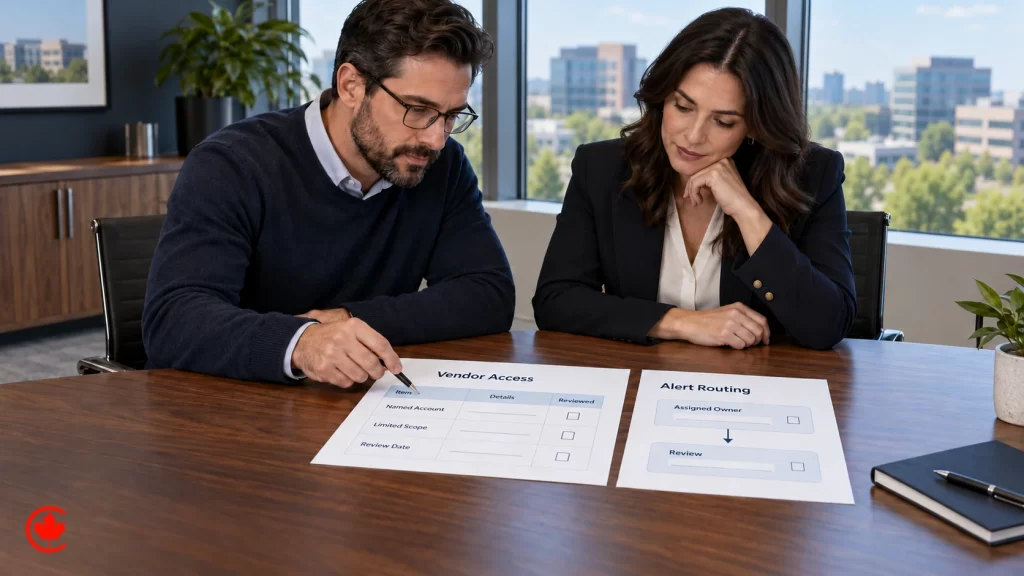
Vendor and contractor access
The camera company, the phone system installer, the practice software vendor and the IT person from three years ago may all have ways in. Vendor access is reviewed account by account. Each outside party gets its own named account, access only to the systems it services, and ideally a connection that is switched on when they need it and off when they finish, with a record of the session. Accounts for vendors you no longer use are removed.
Logging, alerting and DNS filtering
A network that keeps no records cannot answer basic questions after something odd happens: which device connected, when, and to where. Logging and alerting make the network’s activity visible to the person responsible for it.
What gets logged
The firewall, VPN and wireless controllers can record sign-ins, blocked connections, configuration changes and unusual traffic. Logs are kept for a period the organization chooses, stored somewhere they cannot be quietly edited, and reviewed on a schedule. For organizations with privacy obligations, logs help reconstruct what happened, which matters when deciding whether an incident must be reported.
Alerts that reach a person
An alert is only useful if it goes to someone who will read it. The plan names who receives each kind of alert, such as a firewall configuration change, repeated failed VPN sign-ins or a new device on the management segment, and what they should do. Handing alert watching to an outside analyst team is a separate service, described on our managed detection and response page.
DNS filtering
Every time a device visits a website, it first looks up the address through DNS. DNS filtering checks those lookups against lists of known harmful or unwanted sites and blocks them before a connection is made. It covers every device on the network, including ones that cannot run their own protection, such as cameras and smart TVs, and it can extend to laptops when staff are away from the office.
Small offices and several locations
A single office with a handful of desks and an organization with a head office, a warehouse and three storefronts both need network security, but the decisions differ.
The small office
A small office usually needs one properly configured firewall, separate staff and guest Wi-Fi, a segment for printers and any cameras, MFA on remote access, DNS filtering and a simple diagram. The main decisions are whether to replace the internet provider’s router, how staff at home will connect, and who will hold the admin passwords.
Organizations with several sites
With several locations, the questions grow: should branches connect to head office over secure tunnels, or should each site reach cloud applications directly? Are the segments the same at every site, so a technician knows the camera network at the Mississauga store matches the one in Ottawa? Is there one place to see the firewalls at all sites? Consistent naming, matching segment layouts and a central record of every site’s gear make a multi location network manageable.
Opening or moving a location
A new branch or an office move is the easiest moment to get the network right, because nothing is running yet. Building the segments, Wi-Fi and firewall rules before staff arrive avoids the slow retrofit that happens when security is added to a network already in daily use. Our managed IT services team can carry the day to day running of the network after the move.
Diagrams and documentation in your name
Network documentation is often the deliverable owners value most once they have it. Without it, every new provider starts by guessing, and the organization depends on whoever set things up.
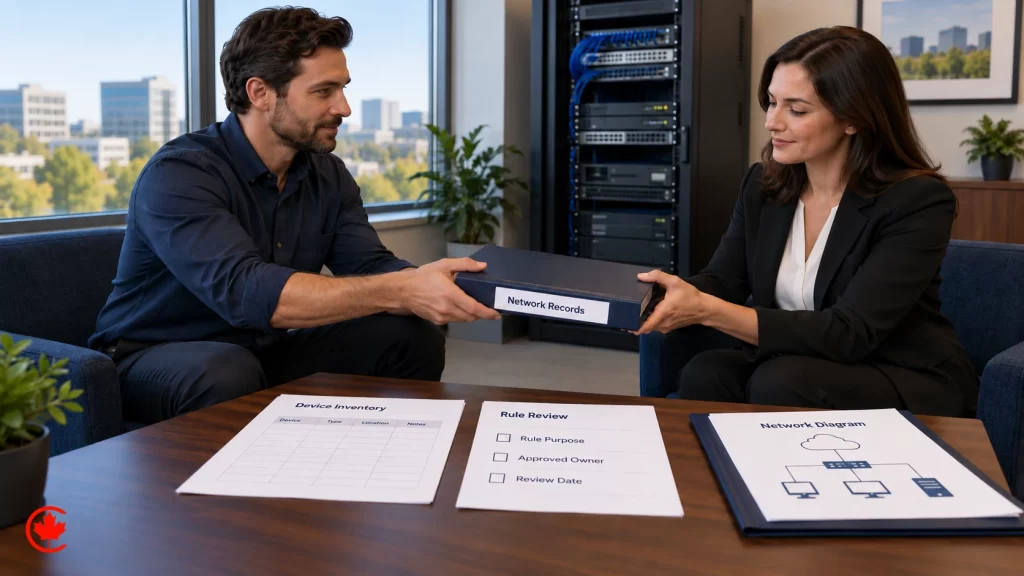
What the documentation set includes
- A network diagram showing the internet connection, firewall, switches, access points and each segment.
- An inventory of network devices with model, location, firmware version and support status.
- The firewall rule list with a plain reason for each rule.
- Wi-Fi networks, what each one reaches and how its passwords or sign-ins are managed.
- Remote access methods, who has access and how MFA is set up.
- Vendor accounts, what each vendor can reach and who approves their sessions.
- Where admin credentials are stored and who can retrieve them.
Admin access stays with the owner
Admin accounts for the firewall, the wireless controller, DNS filtering and any cloud management portal are created in the organization’s name, with credentials kept in a password vault the organization controls. If you change providers, the next one receives the keys from you, not from us.
Where this work starts and stops
Network security covers the design, setup and upkeep of the network itself. Several related jobs sit beside it and are scoped separately.
Testing is a separate job
Setting up a network and testing it are different tasks, and it is healthier when the tester is checking work they did not build. Trying to break in on purpose, with written permission, is described on our penetration testing services page. Regular automated checks for known weaknesses are covered on our forthcoming Vulnerability scanning page.
Devices and the cloud
Protection running on each laptop and phone is the subject of our Endpoint security page, also new in this series. Settings inside cloud services, such as sharing rules and admin roles, are handled through cloud security configuration. Staff habits, such as spotting a fake sign-in page, are the job of security awareness training.
Starting with an overall picture
Organizations unsure where the network sits among their other gaps sometimes begin with a security audit and gap report, which scores the whole environment and ranks the network work against everything else.
Privacy rules and card terminals
Network decisions affect how personal information is protected and what an organization must do if something goes wrong. A few rules are worth having in mind when planning.
Privacy law
If something does go wrong on the network, the first question is often whether outsiders reached personal information. Federal privacy law, PIPEDA, says a breach of security safeguards that creates a real risk of significant harm has to be reported to the Privacy Commissioner of Canada and to the individuals affected, and that a record is kept of every breach. Firewall, VPN and Wi-Fi logs are frequently what answer the reach question. Organizations operating in Quebec have further duties under Law 25, and Ontario health information custodians work under PHIPA, so clinics tend to plan segments around where charting systems sit.
Card terminals and PCI DSS
Businesses that accept cards follow the PCI DSS standard, set by the card industry, which has requirements about how payment systems sit on a network. Keeping card terminals on their own segment is part of how many merchants approach this. Our compliance support page covers PCI DSS and related frameworks in more depth.
Authorization
We only work on networks the client owns or has written authorization to change, and any testing needs written authorization from the system owner. This is a marketing observation, not legal advice.
How a network security project runs
A free review
We start with a conversation about the office or offices: how many locations, what internet service, what gear is in the closet, who connects from home, which vendors have access, and whether there are cameras, card terminals or a phone system on the network. A photo of the network closet and the internet provider’s equipment helps.
A custom proposal
You receive a custom proposal listing what will change: firewall setup or rule cleanup, the segments, Wi-Fi changes, remote access and MFA, firmware updates, logging, DNS filtering and documentation. Fees are quoted in writing, with any hardware or software subscriptions shown on their own line and paid in the organization’s name.
The work
Changes that could interrupt staff are scheduled after hours, with a written list of what to test the next morning. Each change is recorded in the documentation as it happens rather than at the end.
Ongoing upkeep and monthly reporting
Where ongoing upkeep is part of the plan, you receive a monthly report covering firmware updates applied, firewall rule changes and who approved them, notable alerts and what was done, and any equipment nearing the end of its supported life.
What network security costs in Toronto and what changes the fee
Network security work is quoted in writing after the free review. Firewalls, access points, switches and any filtering or management subscriptions are paid to the vendor in the organization’s name and listed separately from our fees.
What drives the quote
- How many locations, and whether they need to connect to each other.
- Whether the existing firewall and access points can be kept or need replacing.
- How many segments are needed, and how many devices must be moved and retested.
- How many people connect from outside, and whether the move is to VPN or to zero trust access.
- How many vendors hold access that needs to be reviewed and rebuilt.
- How much documentation exists today, and how much has to be discovered from scratch.
- Whether the engagement is a one time project or includes ongoing upkeep and monthly reports.
A single office replacing its provider’s router and splitting guest Wi-Fi from staff is a smaller scope than a retail group bringing five stores onto matching segments with central management.
How to compare network security companies in Toronto
A network provider ends up holding the keys to the building’s digital doors, so the questions are worth asking before any work starts.
- Who owns the accounts? The answer should be you, including the firewall admin account, the wireless controller and every management portal.
- Will I receive a network diagram and a firewall rule list with reasons, and in what format?
- How will you segment card terminals, cameras and guest Wi-Fi, and what will you test after each change?
- How will vendors and contractors get access, and how is it switched off?
- Who receives alerts, and what is expected of them?
- Will hardware and subscriptions be bought in my organization’s name?
- Who tests the network, and is it someone other than the person who built it?
- Are the reviews real? Read Google reviews from other organizations before you hand over the keys.
Signs of a weak answer
Be cautious when a provider keeps admin passwords to themselves, cannot explain a firewall rule in plain words, promises that a single box will make the office secure, or treats documentation as something extra. A good provider expects the next provider to read their work.
Related guide: what to check before hiring a cyber security company.
Book a network security review and custom proposal
Before the call, it helps to photograph the network closet and the internet provider’s box, and to jot down every outside company that has ever had a login to your systems: the camera installer, the phone system vendor, an old IT contractor. With that in hand, Canada Create can walk you through your firewall rules, segments, Wi-Fi and remote access in a free network security review, and a custom proposal with fees quoted in writing comes after.
Call (416) 273-9030, Monday to Friday, 9 am to 6 pm, and Saturday, 10 am to 2 pm. After hours, our 24/7 AI agent answers the toll-free line, +1 (800) 808-9235, and we’ll follow up the next business morning.
You can also ask for a network review online. We reply within one business day.
Visit us at 126 Willowdale Avenue, Suite 3, Toronto. We secure office networks across Canada.
Talk to a strategist
Ready when you are?
Request a custom proposal
Tell us your goals, budget and timeline. You get a custom proposal and a named strategist, so your next stage of growth starts now.
Our network security process, from network review to documented handover
Every change is written down, and admin access stays in your organization's name.
- Free review First call
We learn your locations, internet service, gear, remote users and vendors.
- Custom proposal Written proposal
Firewall, segment, Wi-Fi and access changes with fees quoted in writing.
- Network work Agreed milestones
Changes made after hours with a test list for the next morning.
- Upkeep and reporting Every month
Firmware, rule changes and alerts summarized where upkeep is included.
Why organizations choose Canada Create for network security
Since 2008
More than 18 years of websites, search and advertising work for businesses across Canada.
BBB Accredited A+
A BBB Accredited Business with an A+ rating and zero complaints.
Toronto office
126 Willowdale Avenue, Suite 3, Toronto, serving businesses across Canada.
English and French
Our team works in English and French.
Network security in Toronto: questions owners ask
What does network security mean for a small office?
Network security is the work of controlling what can talk to what inside your office, and between the office and the internet. It covers the firewall, how the network is split into segments, staff and guest Wi-Fi, remote access for people at home, firmware patching on routers, switches and access points, and the records of how everything is set up. The software on each laptop is a separate job; this work is about traffic and access.
What does network security actually do in a working office?
It decides which devices can reach each other, which can reach the internet and which outsiders can get in. On a well run network, guest phones cannot see the printers and the card terminal sits on its own segment. Staff working from home come in through a controlled path that asks for a second sign-in step, and alerts go to someone who knows what they mean.
How can I find out how secure our office network is today?
A network review is the usual starting point: someone reads through every firewall rule, checks the segments and Wi-Fi, and lists who has remote and vendor access, then writes up the findings. Plenty of small offices still run on the box their internet provider installed years ago, with default settings and open ports nobody remembers approving. Canada Create prices a review like this in writing once we have talked through your locations and who connects from home.
Which network security setup is best for a small business?
The right setup depends on your headcount, how many segments you need, whether staff connect from home, whether there are cameras or a phone system, and what internet service feeds the building. Whatever the size, look for a firewall that denies traffic by default, separate segments for guests, card terminals and cameras, and multi factor authentication on remote access. When you compare providers, ask who does the hands-on work and whether the diagram and admin access will sit in your organization's name.
What is a network security key on office Wi-Fi?
A network security key is the password a device needs to join a wireless network. On a home router it is often printed on a label on the unit, while in an office it is held by whoever manages the Wi-Fi. A tidy office network keeps one key for staff and a different one for guests, and records where each credential is stored in documentation the organization owns.
Should guests and staff use different network security keys?
Yes. Separate wireless networks with separate passwords keep visitors' phones away from printers, shared files and payment terminals. In clinics, waiting rooms and storefronts, the guest network should also stop one visitor's device from seeing another, and both networks should use current encryption.
What role does the firewall play in network security?
The firewall is the gate between your network and the internet, and often between segments inside the office too. Configured properly, it blocks traffic by default and allows only what has a written reason beside it. On an existing setup every rule gets checked and justified, and on a new install the admin account is created in the organization's name with a strong password and a second sign-in step.
What are some everyday examples of network security controls?
Typical examples are a deny by default firewall, separate segments for staff, guests, card terminals, cameras and servers, isolated guest Wi-Fi, and a VPN or zero trust access with MFA for remote staff. Scheduled firmware updates, logs with alerts routed to a named person, and DNS filtering that blocks harmful sites at lookup round out the set. Each one is recorded on a network diagram and device list kept in your name.


Know what is on your network
A new office, a new insurer questionnaire or a vendor you no longer use is a good moment to find out what your firewall allows. A short review turns it into a written list of changes. Book a free network security review.