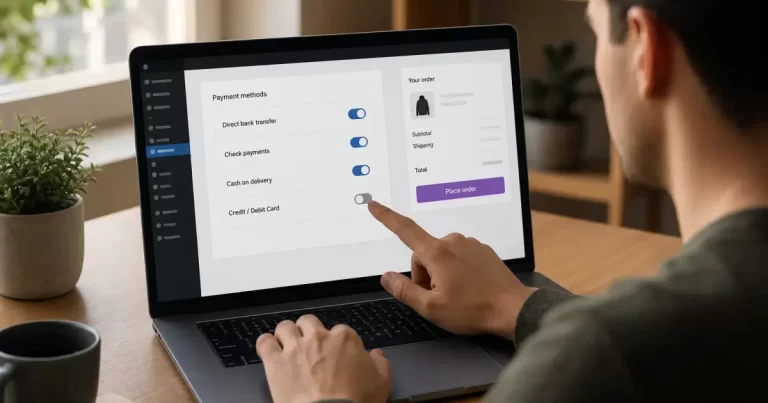
Running unmaintained extensions on a small business website introduces real security exposures, but blindly clicking bulk update can create equally severe operational disruptions. Outdated WordPress plugins often contain unresolved bugs, unpatched security flaws, or architectural gaps that conflict with modern hosting environments. At the same time, updating complex tools without testing can corrupt transactional workflows or break key integrations.
Instead of treating plugin alerts as quick tasks to clear during odd hours, website owners need an orderly assessment process. Evaluating technical exposure, dependencies, and replacement criteria protects site stability. By categorizing plugins based on operational risk, verifying backups before making adjustments, and systematically testing changes on staging copies, you keep your digital storefront resilient against both malicious attacks and update-induced downtime.
Understanding Why Outdated Plugins Introduce Operational Risk
Plugins function by running custom application scripts directly within your content management framework. According to the WordPress.org Manage Plugins documentation, plugins are additional pieces of software written in PHP that extend WordPress core. Because core software focuses on primary user management and publishing tools while leaving custom features to third-party developers, any flaw in an extension operates with the same underlying system access as the core application itself.
When an extension author abandons maintenance, several problems develop simultaneously. Security researchers may discover flaws that automated scanner bots exploit across the web. Modern server environments continuously retire obsolete script interpretations, which can trigger critical system errors if legacy plugins rely on retired syntax. Furthermore, as official core releases introduce architectural improvements, unmaintained plugins may fail silently or produce fatal script interruptions. Keeping extensions current is a baseline operational necessity, but rapid updates must not outpace proper impact analysis.
Triage: Active Tools, Dormant Features, and Inactive Plugins
Before planning updates or replacements, catalogue your inventory based on business necessity and execution context. A common mistake is leaving unused software installed under the assumption that deactivation eliminates operational threats. However, dormant plugin files stored on your server still occupy storage space and remain susceptible to direct file execution or inclusion attacks if specific vulnerabilities exist.
Divide your plugin roster into three operational tiers:
- Revenue-Critical Extensions: E-commerce carts, transaction processors, CRM sync connectors, and booking engines. Any outage here directly stalls revenue.
- Administrative and Marketing Enhancements: Contact forms, SEO tools, analytics tags, and editorial aids. Failure degrades secondary processes without immediately halting sales.
- Unused or Inactive Plugins: Deactivated extensions, design experiments, and discontinued feature tests. These provide no active value and should be queued for prompt removal.
If you manage scheduled processes or complex maintenance schedules, review how you control WordPress automatic updates so critical business extensions never update during peak operational windows without prior review.
Evaluating Developer Health and Abandonment Indicators
Not all update alerts signify immediate danger, and conversely, the absence of an update badge does not confirm safety. Official documentation on the WordPress.org Dashboard Updates screen explains that the administration area checks repositories to show when an installed plugin has a newer version available. However, if a developer ceases development entirely, the directory will register no new version, leaving your site unaware that maintenance has ended.
Review the public extension repository profile or developer changelog for each questionable plugin. Check the release frequency over the preceding two years. If a component has not received an update or compatibility validation across multiple core cycles, it is functionally abandoned. Similarly, verify whether open community support threads show unresolved defect complaints or unaddressed vulnerability notices. If a tool displays no maintenance activity and the author is unresponsive, begin vetting modern replacements rather than hoping for an eventual patch.
The Staging Verification Sequence
Test significant updates or replacements on an isolated staging copy with a verified rollback plan. For an urgent security fix, balance testing time against exposure and use the safest supported containment or deployment path.
Follow this exact implementation order:
- Generate an Isolated Staging Site: Duplicate your production environment, ensuring caching systems and live payment APIs are placed into testing modes.
- Create Restorable Backups: Confirm that you possess a verified database snapshot and file archive prior to modifying the test environment.
- Review Release Notes: Examine the developer changelog for breaking changes, database migrations, or structural deprecations.
- Apply Changes Individually: Update or replace one plugin at a time so any functional failure can be attributed immediately to a specific code change.
- Execute Smoke Tests: Traverse critical customer pathways to verify functional parity before replicating the procedure on the live environment.
Hypothetical Worked Plan: Evaluating a Legacy Custom Inquiry Form
To understand this decision model, consider a hypothetical operational review for an established regional logistics service. The website relies on an unbranded form plugin installed years ago to calculate freight estimates. The plugin has not received an update in twenty-four months, does not support modern core conventions, and throws warning logs on current server setups.
The business owner creates a structured replacement plan rather than abruptly deleting the module:
| Assessment Step | Observed Condition | Planned Action |
|---|---|---|
| Code Evaluation | Plugin relies on outdated script libraries | Flag for complete replacement rather than manual code patching |
| Data Mapping | Historical customer requests stored in a custom database table | Export database records to an archival format before removing software |
| Candidate Testing | Two modern form engines tested in a staging sandbox | Evaluate input validation, webhook dispatch, and notification delivery |
| Parallel Staging Run | Submissions processed simultaneously on an internal test page | Confirm customer inputs match required fields without data loss |
Canada Create™ builds and optimizes WordPress sites for Toronto businesses. Tell us your goals and we will recommend the right setup.
During the verification run on the staging site, the team executes explicit failure checks: intentionally submitting malformed email addresses, testing file upload size constraints, and checking dispatch logs. Only after the candidate form builder proves stable across these boundary checks is the legacy form decommissioned on production.
Verification Checklist and Failure Diagnostics
Relying on a visual scan of your homepage is insufficient when verifying plugin updates or replacements. Changes can break background scripts, scheduled tasks, or database records without altering the basic template layout. Run through this checklist on staging and live installations:
- Administrative Notification Checks: Confirm that core admin pages load without rendering PHP warnings or broken styles.
- Customer Path Validation: Complete a full transaction or submission, verifying that confirmation screens and receipt emails trigger properly.
- System Error Logs: Inspect your web server error logs for fatal interruptions, memory exhaustions, or unhandled exceptions immediately following the update.
- Scheduled Tasks Execution: Check that background processes, such as database cleanups or syndication feeds, continue to fire at their scheduled intervals.
- Rollback Read Readiness: Confirm that your hosting control panel or backup tool allows a point-in-time recovery if an undetected defect emerges hours later.
Establishing a Sustainable Plugin Review Routine
Website security is not a single project that reaches completion; it requires a repeatable business workflow. Schedule a thorough plugin audit once every quarter. Use that session to delete deactivated extensions, assess software maintenance status, and retire redundant tools that can be handled through core functionality or lighter scripts.
Before you begin updating extensions on your live platform today, select your single oldest, least-maintained plugin. Create an isolated backup, duplicate your installation to a staging sandbox, and check the developer changelog to determine whether a straightforward update or a measured replacement strategy best serves your operational stability.
Frequently Asked Questions
Are outdated WordPress plugins dangerous?
Yes; unpatched plugins are the main cause of hacks.
How do I check plugin risk?
Review update history and vulnerability databases.
Should I replace abandoned plugins?
Yes, with maintained alternatives.
Who can audit my plugins?
Our website maintenance service.